SailPoint Identity-Security-Administrator SailPoint Certified Identity Security Administrator Exam Practice Test
Total 99 questions
SailPoint Certified Identity Security Administrator Questions and Answers
Is this a valid way to set-up role assignment criteria?
Proposed Solution / Statement:
A list of Excluded Identities can be defined to prevent specific identities from receiving the role membership.
Does this proposed solution meet the requirement / solve the scenario?
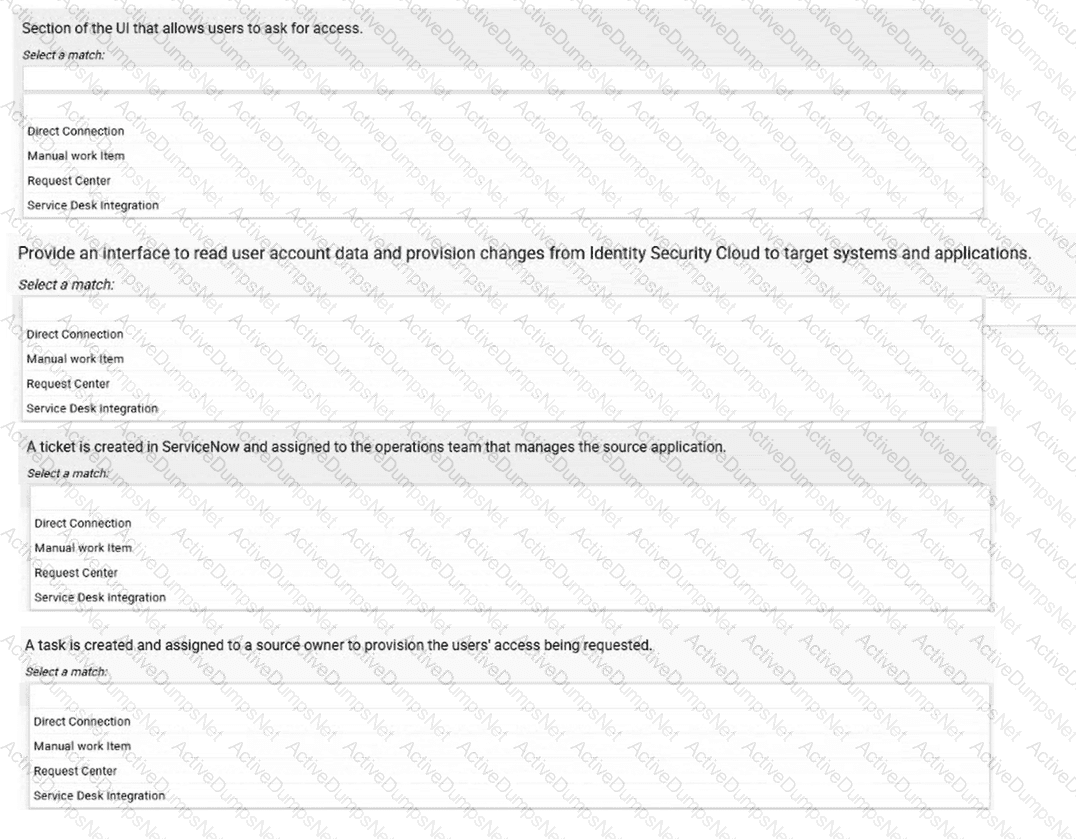
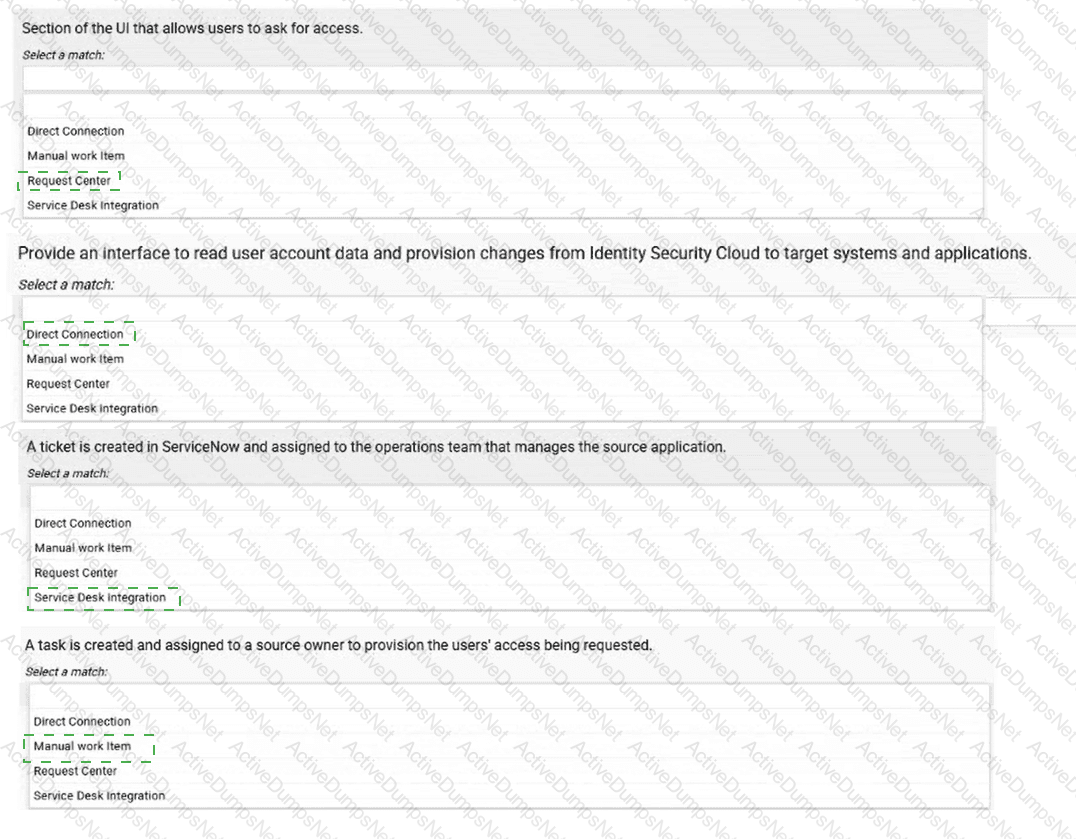
Match the following descriptions with their appropriate definition.
Is this a valid statement regarding role management?
Proposed Solution / Statement:
Adding an entitlement to an existing role provisions an entitlement on all the identities that are currently a member of the role.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid purpose for creating an identity profile?
Proposed Solution / Statement:
To assign specific permissions or access to users based on roles.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid scenario where a Separation of Duties policy should be used?
Proposed Solution / Statement:
A user requests a major system configuration and approves the change.
Does this proposed solution meet the requirement / solve the scenario?
Is the following statement regarding different account aggregation types true?
Proposed Solution / Statement:
Disabling optimization during aggregation forces the system to process all accounts.
Does this proposed solution meet the requirement / solve the scenario?
Reference the following search query:
created:[now-24h TO now] AND (@access(displayName:New_Hire_Access) OR @access(source.name:Acme_HRMS)) AND @entitlements(name:Manager_Access)
Is this statement true about the search query above?
Proposed Solution / Statement:
Removing the AND @entitlements(name:Manager_Access) from the query makes it valid, returning users who were created within the last 24 hours and either have access to the source Acme_HRMS or have the New_Hire_Access access profile assigned.
Does this proposed solution meet the requirement / solve the scenario?
As part of the organization's update to its access request approval and notification process, does the following statement accurately reflect the global reminder and escalation policy?
Proposed Solution / Statement:
If reviewers do not complete their reviews within the specified timeframe, the request will automatically be escalated to a new reviewer; this escalation process can occur up to three times.
Does this proposed solution meet the requirement / solve the scenario?
Is the following statement about Workflow components valid?
Proposed Solution / Statement:
Every action name (not display name) in a workflow must be unique.
Does this proposed solution meet the requirement / solve the scenario?
Users are complaining that they would like to request access to groups that have recently been added to the Corporate Directory system, but they are unable to see them. The system feature Enable Entitlement Requests has been enabled and access request segments have not been enabled.
Is this a valid step to debug the problem?
Proposed Solution / Statement:
Open the source configuration and navigate to the Entitlements page to search for the group and verify the Requestable status.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement about identity profile?
Proposed Solution / Statement:
Once users are assigned to an identity profile, administrators cannot modify or delete the identity profile.
Does this proposed solution meet the requirement / solve the scenario?
Assuming an access item's approval type is set to "reviewer," does the following statement accurately describe the approval flow behavior?
Proposed Solution / Statement:
When a user requests access for themselves and they are also in the approval chain, the approval flow will route to their manager instead to prevent a conflict of interest.
Does this proposed solution meet the requirement / solve the scenario?
Does this statement accurately describe the purpose of the Virtual Appliance (VA)?
Proposed Solution / Statement:
The VA eliminates the need for databases to store Personally Identifiable Information (PII).
Does this proposed solution meet the requirement / solve the scenario?
A newly created entitlement is not showing up in Identity Security Cloud. An aggregation issue is suspected. The administrator wants to verify what went wrong.
Is this the correct way to troubleshoot the issue?
Proposed Solution / Statement:
Look at the "Entitlement Mapping" settings under the source configuration to confirm that the entitlement schema is correctly defined.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement regarding Identity Security Cloud (ISC) policies?
Proposed Solution / Statement:
Separation of duties policies help prevent users from gaining toxic combinations of access.
Does this proposed solution meet the requirement / solve the scenario?
As part of the organization's update to its access request approval and notification process, does the following statement accurately reflect the global reminder and escalation policy?
Proposed Solution / Statement:
For governance groups, access requests will be sent only to the manager of an active member.
Does this proposed solution meet the requirement / solve the scenario?
Is the following statement about entitlements valid?
Proposed Solution / Statement:
Entitlements represent the specific access rights on a source.
Does this proposed solution meet the requirement / solve the scenario?
Below is a search command in Identity Security Cloud.
Does the description accurately match the outcome of the search command?
Proposed Solution / Statement:
accountCount:[1 to 4
will search for identities that have 1, 2, 3, or 4 accounts.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement regarding uncorrelated accounts?
Proposed Solution / Statement:
An uncorrelated account can be sourced from both authoritative and non-authoritative sources.
Does this proposed solution meet the requirement / solve the scenario?
Is this statement regarding access management valid?
Proposed Solution / Statement:
It is mandatory to make a role requestable.
Does this proposed solution meet the requirement / solve the scenario?
Is this statement true regarding Identity Governance and Administration (IGA)?
Proposed Solution / Statement:
IGA enables security teams to gain access insight and visibility into how users access systems and apply policies and controls to ensure secure access.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement about common authentication methods?
Proposed Solution / Statement:
The Identity Provider and Service Provider in a SAML setup trust each other based on public keys that have been exchanged as part of the configuration.
Does this proposed solution meet the requirement / solve the scenario?
Assuming an access item's approval type is set to "reviewer," does the following statement accurately describe the approval flow behavior?
Proposed Solution / Statement:
When a governance group is set as an approver, the request is automatically approved if the requester is a member of that governance group.
Does this proposed solution meet the requirement / solve the scenario?
Does this statement correctly describe a function of the Virtual Appliance (VA)?
Proposed Solution / Statement:
The VAs initiate communication to the VA cluster queue in the Identity Security Cloud tenant.
Does this proposed solution meet the requirement / solve the scenario?
Is the following a valid configuration item for the identity profile's sign-in and security settings?
Proposed Solution / Statement:
If Multifactor Authentication is configured, the users of the Identity Profile must provide proof of their identity in two ways before they are allowed to unlock their account or reset their password.
Does this proposed solution meet the requirement / solve the scenario?
An organization must maintain both production and sandbox tenants of Identity Security Cloud. The administrator needs to maintain consistent configurations across both environments, and backup and restore from previous configuration backups.
Does the following statement accurately describe how Configuration Hub functionality can help in this scenario?
Proposed Solution / Statement:
Configuration Hub allows one to create configuration templates that can be exported and imported across tenants.
Does this proposed solution meet the requirement / solve the scenario?
Does this statement accurately describe the purpose of the Virtual Appliance (VA)?
Proposed Solution / Statement:
The VA allows the tenant to connect to on-prem sources.
Does this proposed solution meet the requirement / solve the scenario?
An Identity Security Cloud tenant is configured to disable all source accounts for an identity that enters the terminated lifecycle state. A database administrator reports they have been noticing that employees who are terminated, still have their database accounts as "Active" in the source system.
Is this a valid troubleshooting option for the scenario above?
Proposed Solution / Statement:
On the Identity, validate that the Lifecycle State attribute value that is set for the affected users is "Terminated".
Does this proposed solution meet the requirement / solve the scenario?
Does the following event trigger the de-provisioning of a user's access?
Proposed Solution / Statement:
The department of a user changes, and the new department does not have access to an application that was previously assigned.
Does this proposed solution meet the requirement / solve the scenario?
Total 99 questions