Microsoft GH-600 Developing in Agentic AI Systems Exam Practice Test
Developing in Agentic AI Systems Questions and Answers
You have a GitHub repository that uses the GitHub Copilot coding agent to resolve issues in an ephemeral GitHub Actions environment.
Builds fail unless an environment variable named NPM_TOKEN is available, because the repository depends on a private package registry.
A workflow named .github/workflows/copilot-setup-steps.yml was added but was merged into a non-default branch and does NOT run when new agent sessions start.
You need to ensure that for every new agent session, the setup steps run, and the private registry token is available as NPM_TOKEN, without hardcoding secrets in the repository.
What should you do?
A developer uses the GitHub Copilot CLI in plan mode.
Copilot produces a plan.
What does Copilot do next?
You have a GitHub Copilot coding agent that has completed a pull request for a security fix in your repository.
Before merging, you need to evaluate the quality of the agent’s work by using both automated evaluation signals and human review.
You review the session log and the pull request.
What are two automated security scanning signals available for the pull request? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
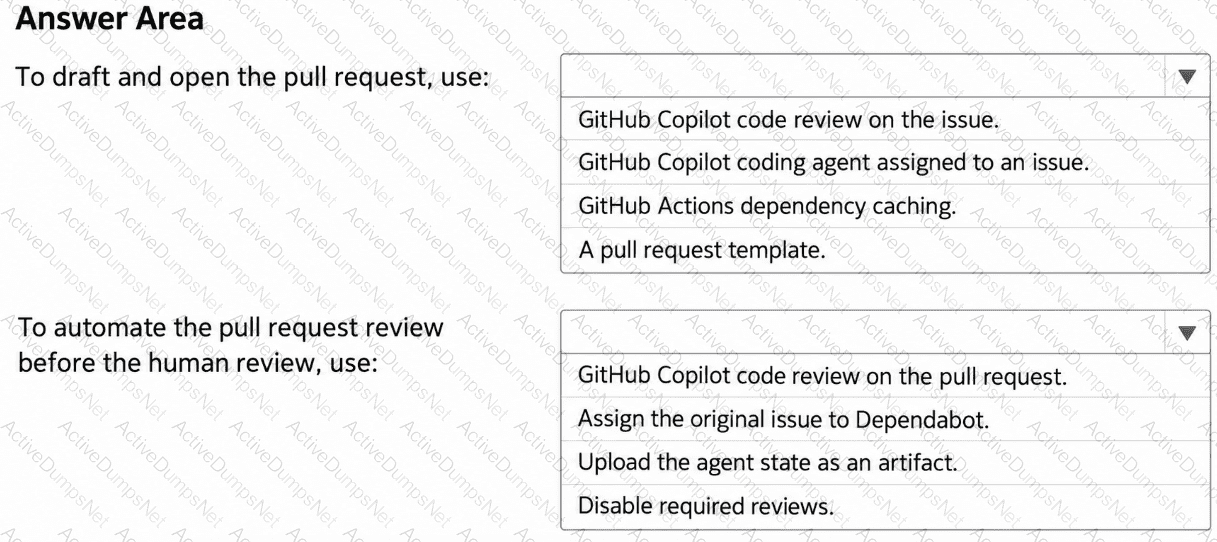
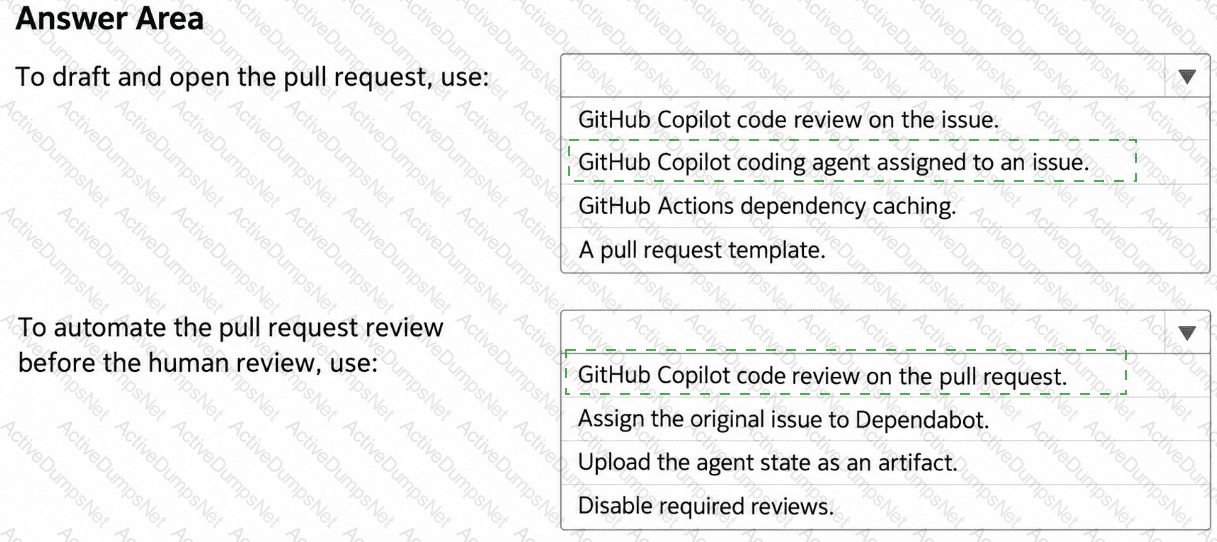
You have a GitHub Enterprise Cloud repository that uses GitHub Actions for CI and requires pull requests for all changes.
You are planning a GitHub Actions workflow where a coding agent drafts implementation changes and tests from GitHub issues, and an automated review runs before human review.
You need the agent to draft changes from an assigned issue, open a pull request, and add an automated review to the pull request before requesting a human review.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
In Microsoft Visual Studio Code, you are using GitHub Copilot Chat to generate documentation for a new feature.
Earlier in the day, you used Copilot Chat extensively for an unrelated refactoring task.
You discover that the Copilot responses for the new documentation task are influenced by the earlier conversation.
You need Copilot to focus only on the current task and avoid using prior conversational context. The solution must NOT affect other conversations.
What should you do?
You have a GitHub repository that uses the GitHub Copilot coding agent to run agent plans for assigned issues.
You discover that some issues contain ambiguous implementation steps.
You need to reduce the likelihood that Copilot executes plans based on ambiguous implementation steps.
What should you do?
You are running the GitHub Copilot CLI and want the agent to execute file edits and shell commands without prompting for confirmation on each individual action, during a trusted throwaway sandbox session. Which flag/command should you use?
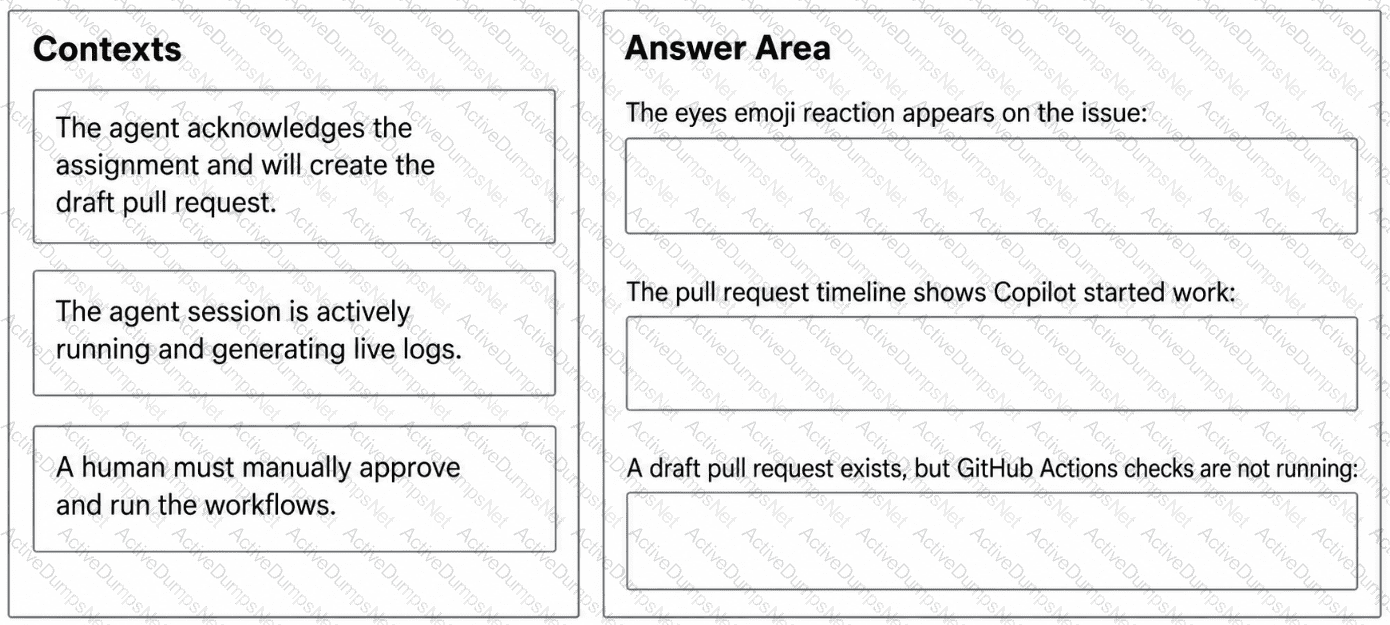
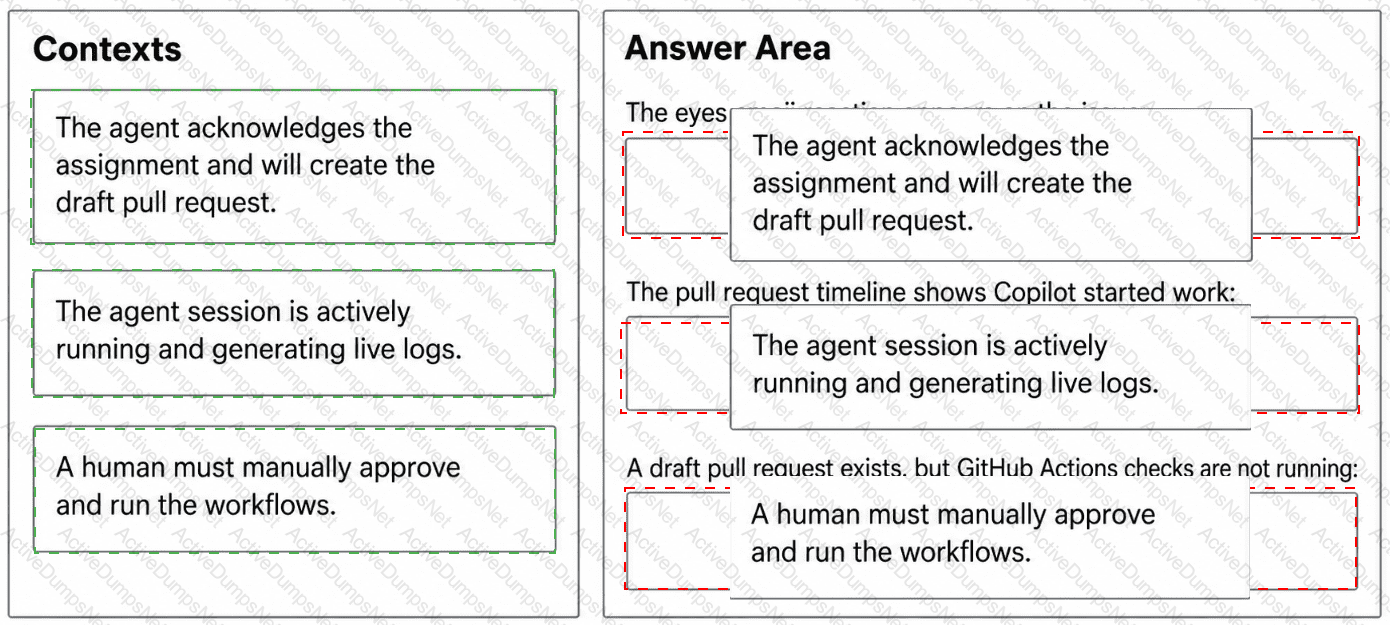
You have a GitHub Enterprise Cloud organization that uses the GitHub Copilot coding agent to resolve issues asynchronously.
When an issue is assigned to GitHub Copilot, the agent creates a draft pull request, but your team cannot always tell whether the agent is actively working, has completed its session, or is awaiting workflow approval.
Which execution context does each signal indicate? To answer, drag the appropriate context to the correct signals.
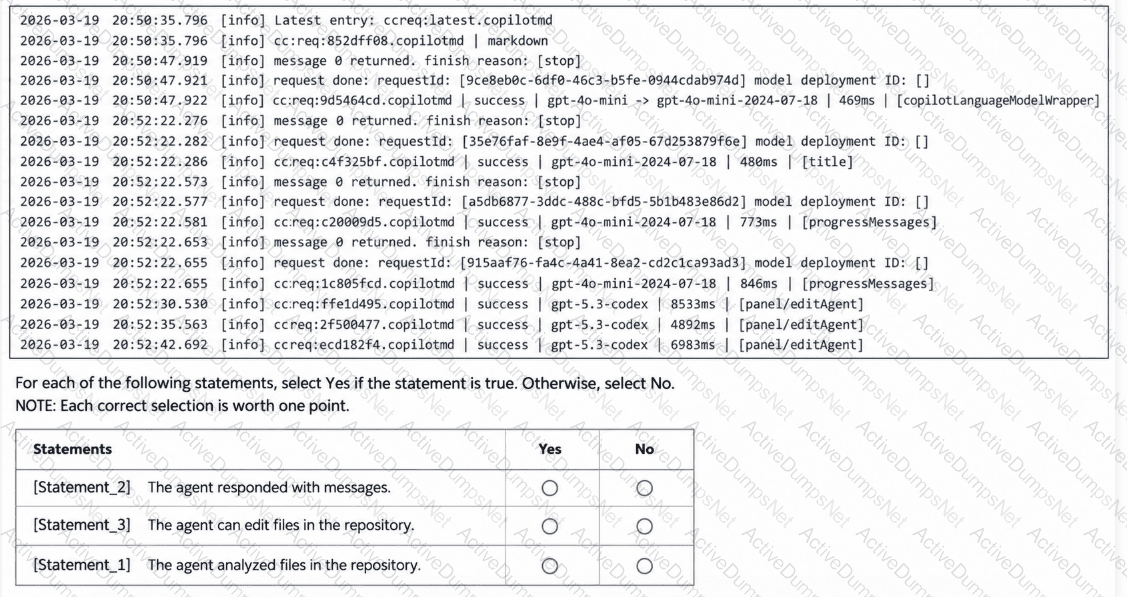
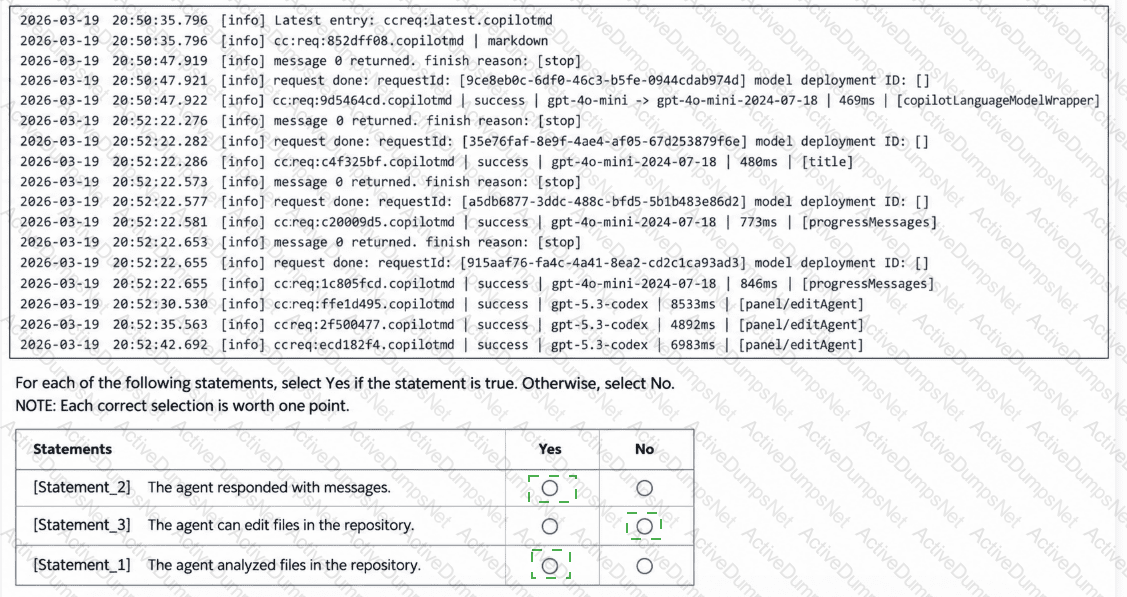
You have the following agent logs.
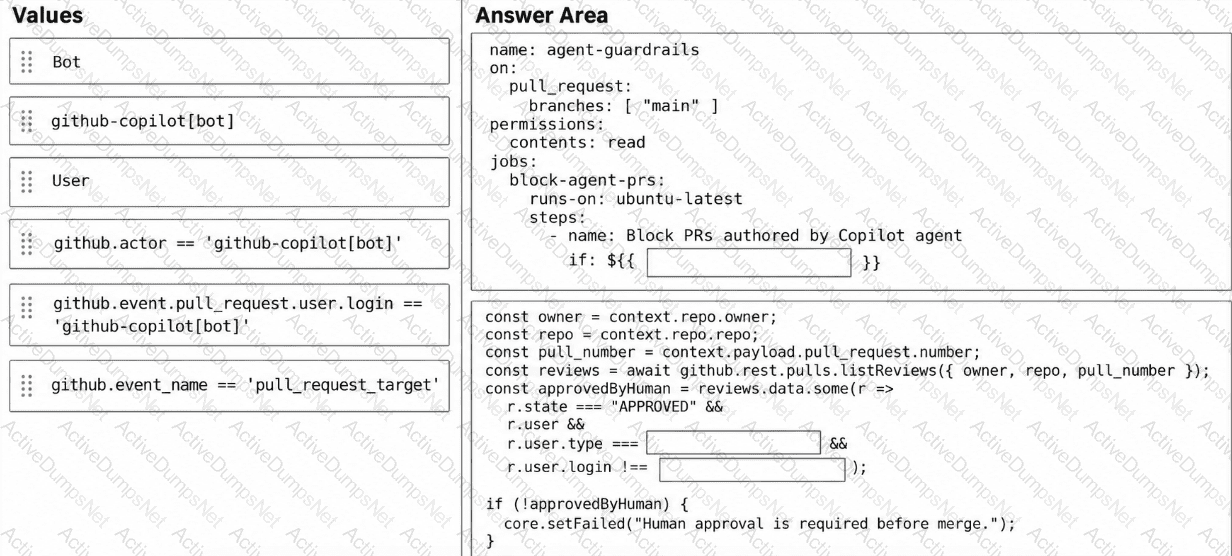
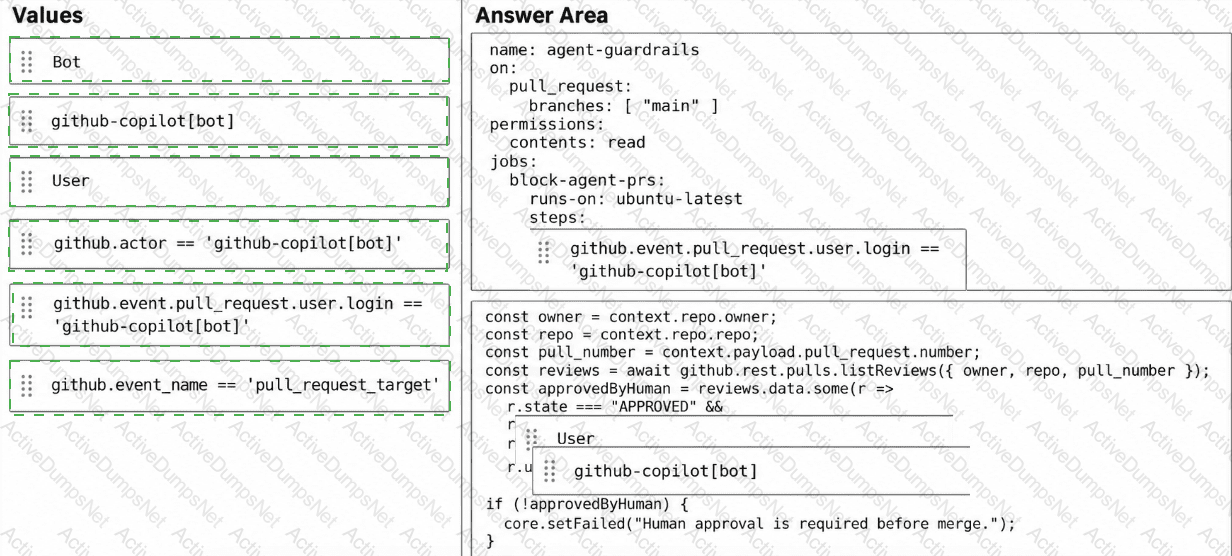
You have a GitHub repository that uses the GitHub Copilot coding agent and GitHub Copilot Chat.
You need to add a GitHub Actions workflow that meets the following requirements:
Blocks merges unless agent changes are reviewed by a human.
Fails if the pull request author is the Copilot coding agent.
How should you complete the workflow? To answer, drag the appropriate values to the correct targets. Each value may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have a GitHub Enterprise Cloud organization that has Copilot agents enabled.
You discover activity in a repository.
You need to identify whether the activity was initiated by an agent.
Which two audit log fields can you use? Each correct answer presents a complete solution.
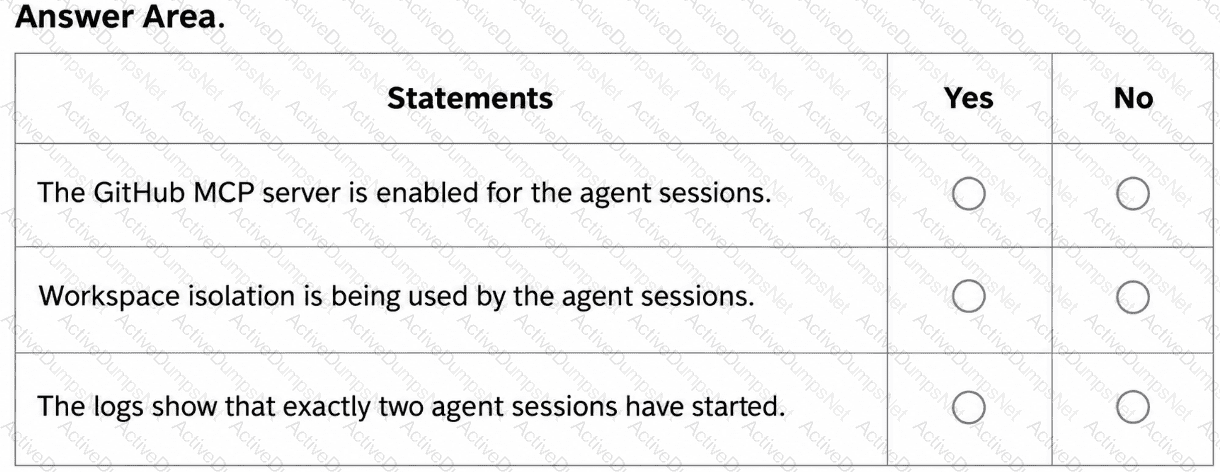
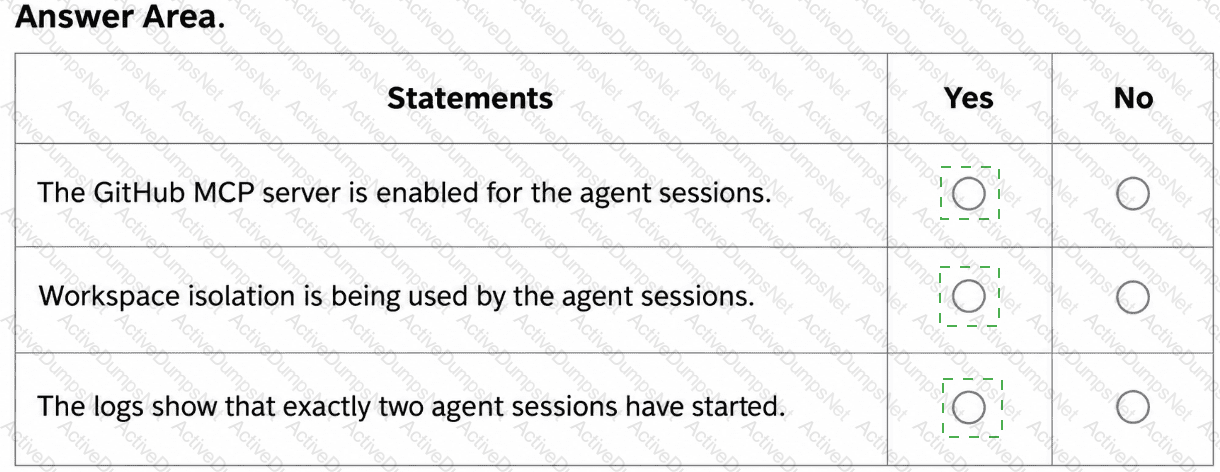
You are evaluating the logs of the multi-agent workflow in repo2.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You need to make changes to repo1 to support the planned changes for the agents.
What should you modify?
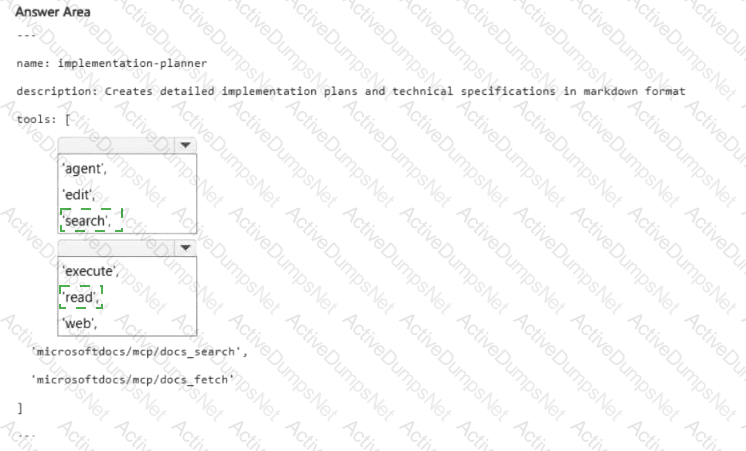
You need to implement agent2 to meet the technical requirements.
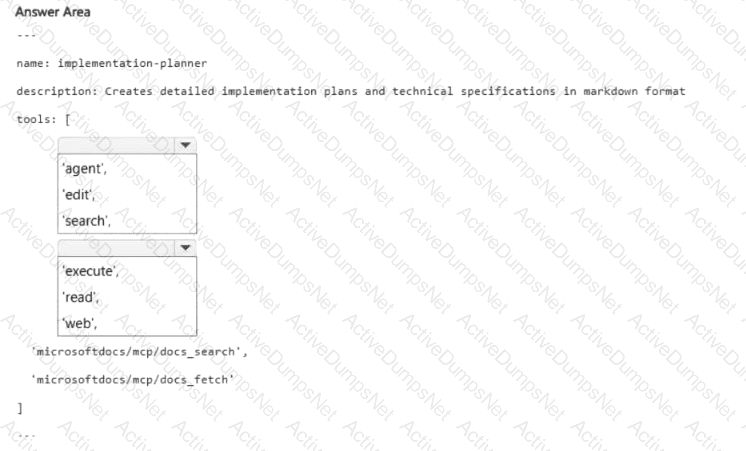
How should you complete the YAML configuration? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
HOTSPOT
name: implementation-planner
description: Creates detailed implementation plans and technical specifications in markdown format
tools: [
< Dropdown 1 > ,
< Dropdown 2 > ,
' microsoftdocs/mcp/docs_search ' ,
' microsoftdocs/mcp/docs_fetch '
]
The accompanying image includes empty dropdown controls and recreated practice alternatives.
You need to troubleshoot the issue reported by Dev1.
What should you review?
While upgrading App1, the agent identifies 47 issues, including a security vulnerability, and 46 API incompatibilities across different projects.
Which two actions are unsafe to delegate to the agent and require human involvement? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
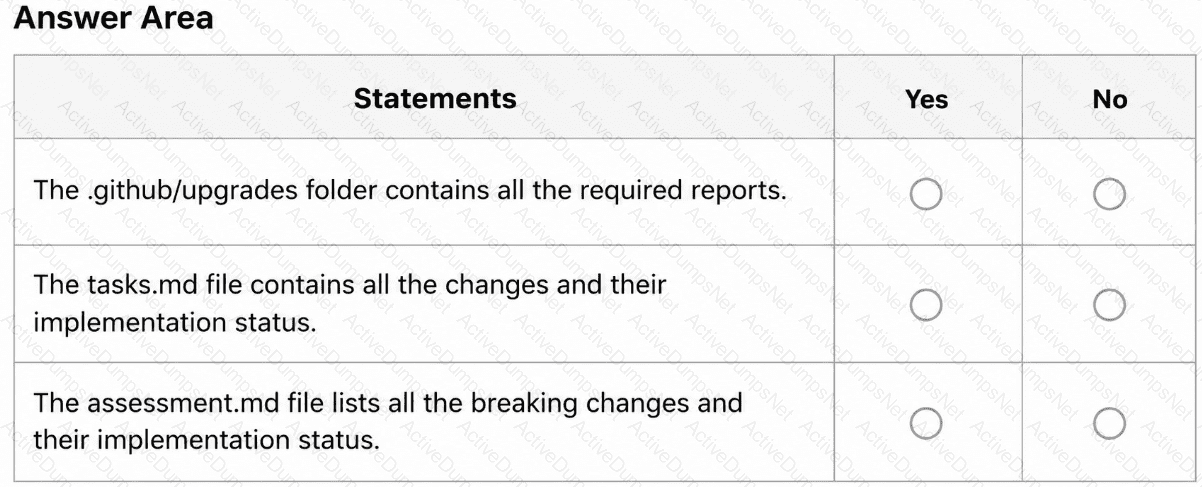
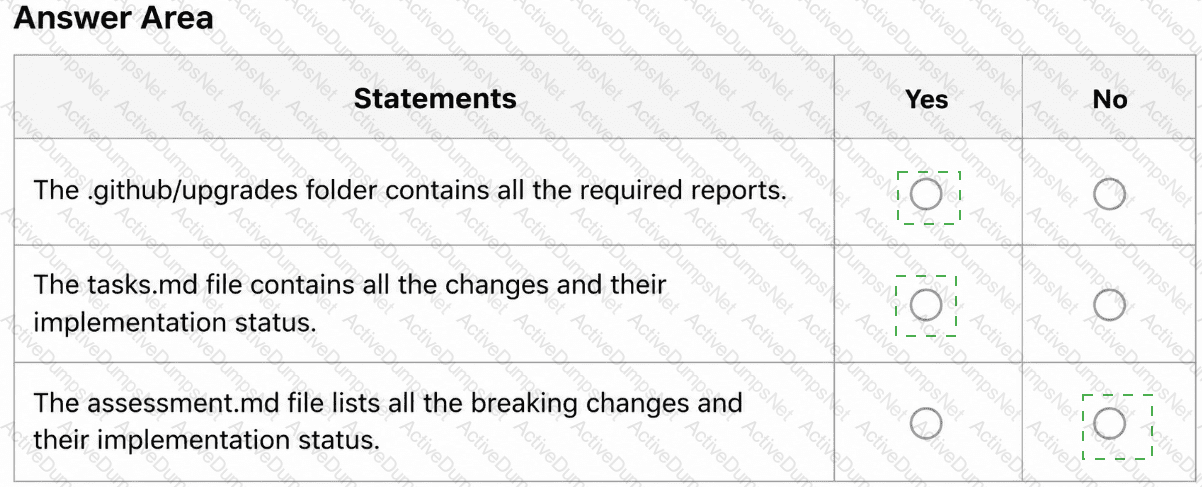
After App1 is upgraded to meet the technical requirements, you need to validate the output.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You need to make changes to repo1 to support the planned changes for the developers.
What should you modify?
Before App1 is upgraded, you need to verify each individual upgrade step and whether all tests have passed.
Which file should you use?
You need to enable Copilot memory to support the planned changes.
What should you configure?
You need to configure agent1 to support the planned changes.
What should you do?
You need to resolve the scoping issue associated to agent1.
What should you do?