Weekend Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: discactive

Fortinet NSEI_OTS_AR-7.6 Fortinet NSE I - OT Security 7.6 Architect Exam Practice Test

Fortinet NSE I - OT Security 7.6 Architect Questions and Answers

Question 1

You want to improve the security of your OT network and therefore deploy a FortiGate device with the OT signatures database. Which two statements about this database are true? (Choose two answers)

Options:

A.

You must install a valid OT security service license.

B.

You must import the OT signatures database manually.

C.

The OT signatures database is enabled by default.

D.

You must set exclude-signatures to none in the console line interface.

Question 2

Refer to the exhibit.

Question # 2

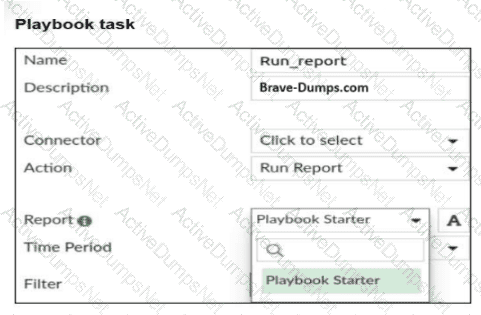
A Run_report task is shown. You want to automate the generation of a newly created report on FortiAnalyzer . When you configure the Run_report task in Playbook, why is the report not shown in the Report field? (Choose two answers)

Options:

A.

You must first configure the connector.

B.

You must first enable Extended Log Filtering in the report.

C.

You must first enable Auto-cache in the report.

D.

You must first configure an event handler.

E.

You must first select Playbook Starter, and then select the newly created report.

Question 3

Refer to the exhibits.

Question # 3

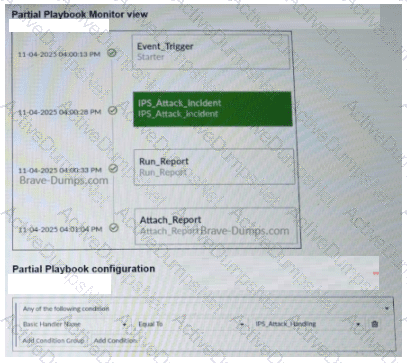
A partial view of the Playbook Monitor page and the corresponding playbook configuration are shown. Based on the monitor page and the configuration of the playbook, what has triggered the Run_Report task? (Choose one answer)

Options:

A.

An IPS_Attack_Handling event

B.

An IPS incident creation

C.

An Event_Trigger log

D.

An IPS_Attack_Incident log

Question 4

What is the main OT component for monitoring and controlling industrial processes? (Choose one answer)

Options:

A.

Programmable Logical Controller (PLC)

B.

Supervisory Control and Data Acquisition (SCADA)

C.

Industrial Control System (ICS)

D.

Industrial Internet of Things (IIoT)

Question 5

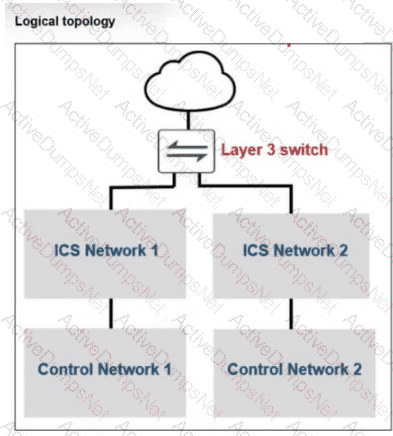
Refer to the exhibit. A partial OT network is shown. You must improve the security of this OT network and implement internal segmentation between network 1 and network 2. How can you achieve the segmentation? (Choose one answer)
Question # 5

Options:

A.

You can configure universal ZTNA.

B.

You can configure one traffic VDOM.

C.

You can configure an explicit software switch.

D.

You can configure forward domain IDs for each network.

Question 6

You would like to customize your current FortiAnalyzer report to provide a better risk assessment of your OT network. Which two options can you use to enhance your report? (Choose two answers)

Options:

A.

The FortiView library

B.

The Datasets library

C.

The Log View library

D.

The Chart library

E.

The Dashboard library

Question 7

Refer to the exhibit.

Question # 7

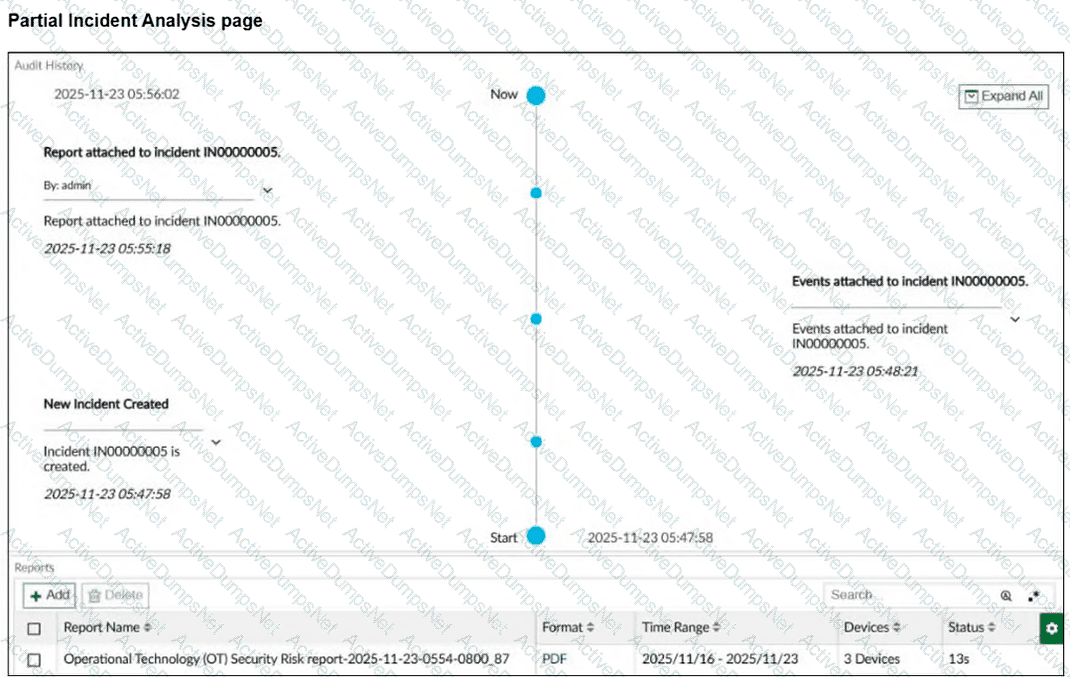
A partial Incident Analysis page is shown. How was the 360-Degree Security Review OT report attached to the incident? (Choose one answer)

Options:

A.

Automatically by a stitch

B.

Automatically by an event handler

C.

Automatically by a playbook

D.

Manually by an administrator

Question 8

Refer to the exhibit.

Question # 8

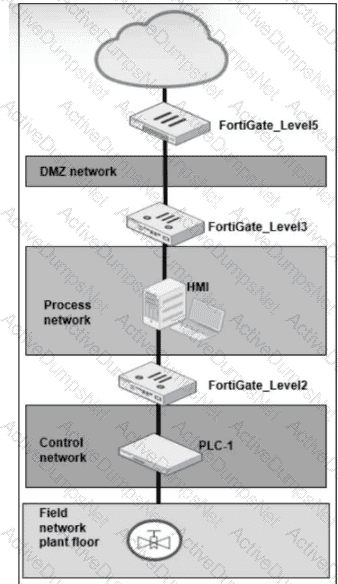
A simplified OT network is shown. You want to optimize the protection of this OT network. Which two controls must you implement? (Choose two answers)

Options:

A.

Offline IDS on FortiGate_Level3.

B.

IPS on FortiGate_Level5.

C.

Virtual patching on FortiGate_Level2.

D.

OT signature on FortiGate_Level5.

Question 9

You want to automate some tasks in your OT network. Which three configurations are directly available in a new basic event handler on FortiAnalyzer? (Choose three answers)

Options:

A.

Send alert email

B.

Create a report

C.

Quarantine an attacker

D.

Automatically create an incident

E.

Automation stitch

Question 10

Refer to the exhibit.

Question # 10

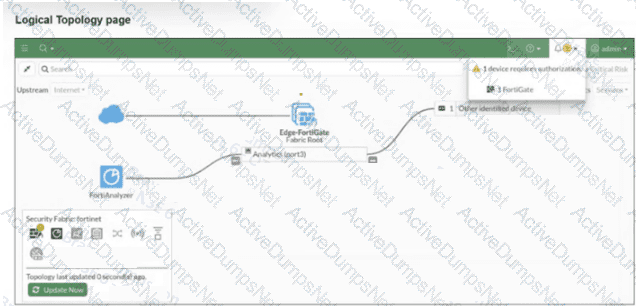
A Logical Topology page of a FortiGate device is shown. Your OT company wants to gain visibility into the network. You decide to implement device detection with the Security Fabric. Based on the exhibit, which statement is correct? (Choose one answer)

Options:

A.

Device Detection is enabled on the other identified device.

B.

The other identified device must be authorized on the root FortiGate.

C.

The other identified device must be authorized on FortiAnalyzer.

D.

Device Detection is enabled on port3.

Question 11

For the installation of your first FortiGate device, you want to minimize the impact in your OT network. Therefore, you deploy it initially as an offline IDS. Which two statements about this deployment are correct? (Choose two answers)

Options:

A.

The FortiGate device acts as a network sensor.

B.

The cybersecurity visibility increases with the security profiles.

C.

Attacks, including zero-day attacks, are blocked.

D.

OT traffic flows through the FortiGate device.

Question 12

Refer to the exhibit.

Question # 12

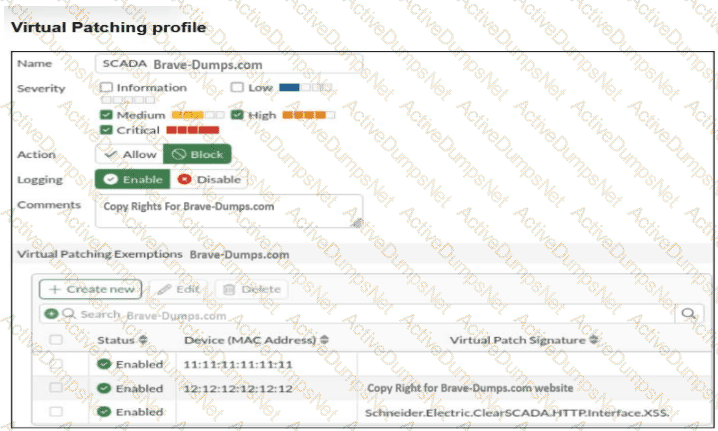
A Virtual Patching profile is shown. You have recently updated your SCADA system and would like to apply the SCADA virtual patching profile. Which two statements about this profile are correct? (Choose two answers)

Options:

A.

Only the vulnerability Schneider.Electric.ClearSCADA.HTTP.Interface.XSS is still present.

B.

Low severity signatures are not blocked for the device with the MAC address 12:12:12:12:12.

C.

This profile blocks critical severity signatures for all the devices.

D.

The device with the MAC address 11:11:11:11:11 is considered to have no vulnerabilities.

Question 13

Refer to the exhibit.

Question # 13

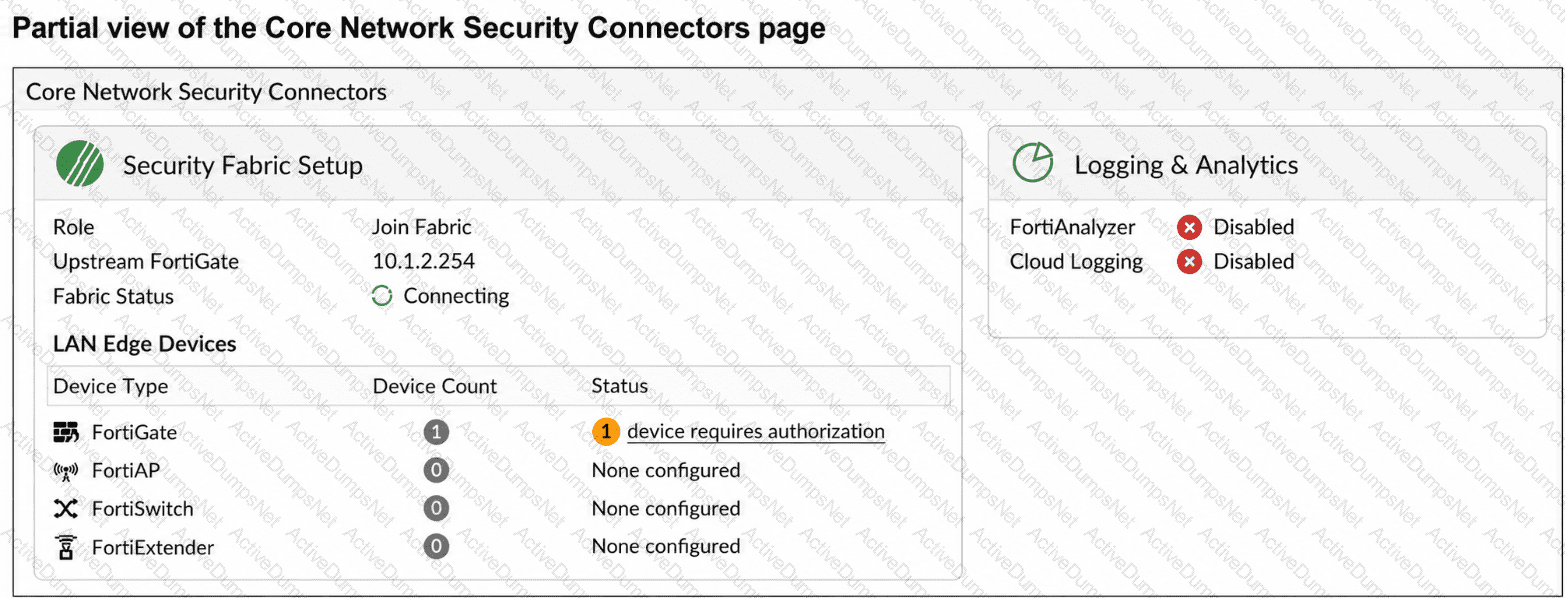
The Core Network Security Connectors page of a FortiGate device is shown. You are configuring the Security Fabric in your OT network. One of the devices is not sending logs to FortiAnalyzer. When you check the status of the FortiGate device, it is Disabled as shown in the exhibit. Which two actions must you perform to enable this FortiGate device to send logs to FortiAnalyzer? (Choose two answers)

Options:

A.

You must configure the Logging & Analytics settings on this FortiGate device.

B.

You must configure the Fabric settings on FortiAnalyzer.

C.

You must authorize this FortiGate device on FortiAnalyzer.

D.

You must authorize this FortiGate device on the root FortiGate.

Question 14

Refer to the exhibit.

Question # 14

Based on the information provided on the partial Event Monitor page shown in the exhibit, how was the attack detected? (Choose one answer)

Options:

A.

Automatically by a stitch

B.

Manually by an administrator

C.

Automatically by a playbook

D.

Automatically by an event handler

Question 15

You want to gain complete visibility of the entire attack surface using FortiAnalyzer.

Which two views must you use to achieve this result? (Choose two.)

Options:

A.

Risk Summary Dashboard

B.

Resources Reports

C.

MITRE ATT & CK® Attack

D.

Analytics Search

E.

SOC Dashboard

Question 16

Refer to the exhibit.

Question # 16

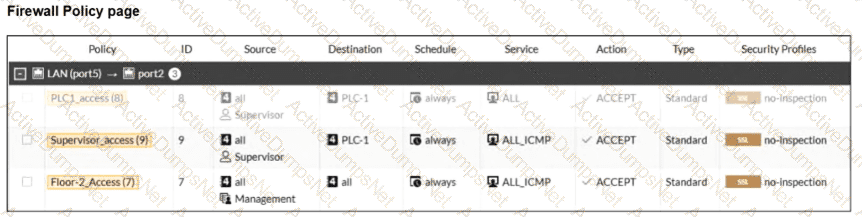
The configuration of firewall policies is shown.

To improve the security of your OT network, you have configured authentication in the firewall policies as shown in the exhibit, with CLI parameters set to their default settings. However, when you test HTTPS access from the LAN subnet to PLC-1, it is successful without any authentication prompt.

What is the reason?

Options:

A.

You did not configure authentication in firewall policy ID 9.

B.

You must first authenticate using a protocol such as HTTP or Telnet.

C.

You are authenticated with the default implicit firewall policy.

D.

You are passively authenticated.