Cisco 350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Exam Practice Test
Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Questions and Answers
When using Cisco AMP for Networks which feature copies a file to the Cisco AMP cloud for analysis?
When a next-generation endpoint security solution is selected for a company, what are two key
deliverables that help justify the implementation? (Choose two.)
Which two services are provided by the Cisco Talos Incident Response group? (Choose two.)
In which type of attack does the attacker insert their machine between two hosts that are communicating with each other?
Which policy does a Cisco Secure Web Appliance use to block or monitor URL requests based on the reputation score?
Which open source tool does Cisco use to create graphical visualizations of network telemetry on Cisco IOS XE devices?
Which security solution protects users leveraging DNS-layer security?
A network engineer must monitor user and device behavior within the on-premises network. This data must be sent to the Cisco Stealthwatch Cloud analytics platform for analysis. What must be done to meet this
requirement using the Ubuntu-based VM appliance deployed in a VMware-based hypervisor?
Which Cisco security solution stops exfiltration using HTTPS?
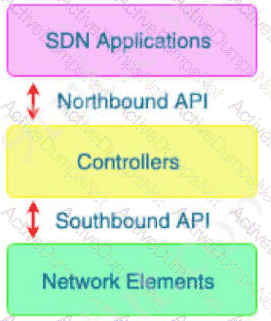
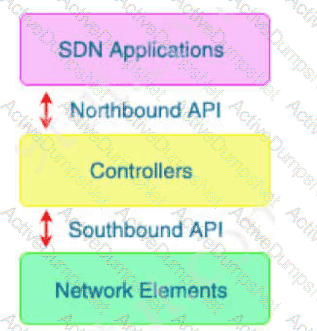
Which type of API is being used when a controller within a software-defined network architecture dynamically
makes configuration changes on switches within the network?
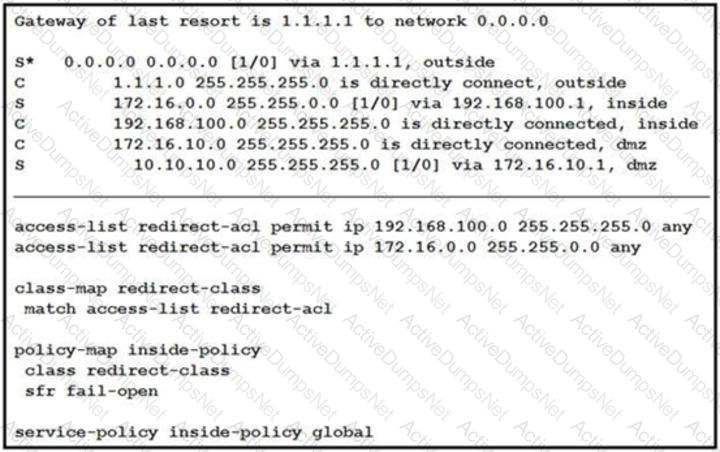
Refer to the exhibit.
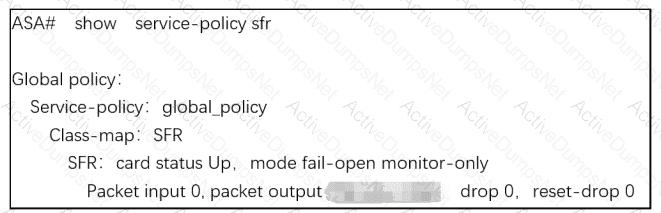
What are two indications of the Cisco Firepower Services Module configuration?
(Choose two.)
A security test performed on one of the applications shows that user input is not validated. Which security vulnerability is the application more susceptible to because of this lack of validation?
Cisco SensorBase gaihers threat information from a variety of Cisco products and services and performs analytics to find patterns on threats Which term describes this process?
An organization has a requirement to collect full metadata information about the traffic going through their AWS cloud services They want to use this information for behavior analytics and statistics Which two actions must be taken to implement this requirement? (Choose two.)
A small organization needs to reduce the VPN bandwidth load on their headend Cisco ASA in order to
ensure that bandwidth is available for VPN users needing access to corporate resources on the10.0.0.0/24 local HQ network. How is this accomplished without adding additional devices to the
network?
A financial services firm is concerned about employees inadvertently pasting sensitive customer account information into public generative AI websites. The security team needs to implement a solution that inspects outbound traffic and prevents the transmission of sensitive data to AI platforms. Which two configuration actions must the administrator perform on Cisco Secure Access to achieve the requirement? (Choose two.)
Which Cisco security solution integrates with cloud applications like Dropbox and Office 365 while protecting data from being exfiltrated?
Which two protocols must be configured to authenticate end users to the Web Security Appliance? (Choose two.)
An organization uses Cisco FMC to centrally manage multiple Cisco FTD devices. The default management
port conflicts with other communications on the network and must be changed. What must be done to ensure
that all devices can communicate together?
What is the function of the Internet Key Exchange (IKE) protocol in an IPsec VPN?
What is a difference between a DoS attack and a DDoS attack?
Which method must be used to connect Cisco Secure Workload to external orchestrators at a client site when the client does not allow incoming connections?
How does Cisco Secure Endpoint provide next-generation protection?
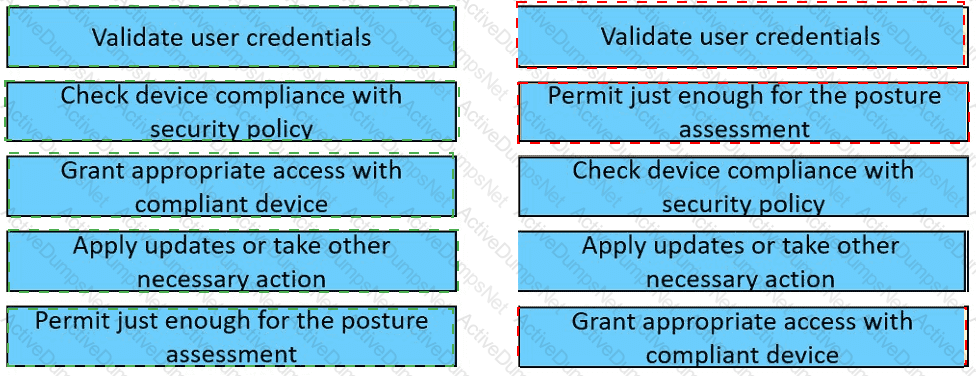
Which posture assessment requirement provides options to the client for remediation and requires the
remediation within a certain timeframe?
An administrator needs to configure the Cisco ASA via ASDM such that the network management system
can actively monitor the host using SNMPv3. Which two tasks must be performed for this configuration?
(Choose two.)
Which open standard underpins OpenID Connect, enabling Cisco Duo to authorize application access?
Which solution for remote workers enables protection, detection, and response on the endpoint against known and unknown threats?
A network engineer has been tasked with adding a new medical device to the network. Cisco ISE is being used as the NAC server, and the new device does not have a supplicant available. What must be done in order to securely connect this device to the network?
A network engineer has configured a NTP server on a Cisco ASA. The Cisco ASA has IP reachability to the
NTP server and is not filtering any traffic. The show ntp association detail command indicates that the
configured NTP server is unsynchronized and has a stratum of 16. What is the cause of this issue?
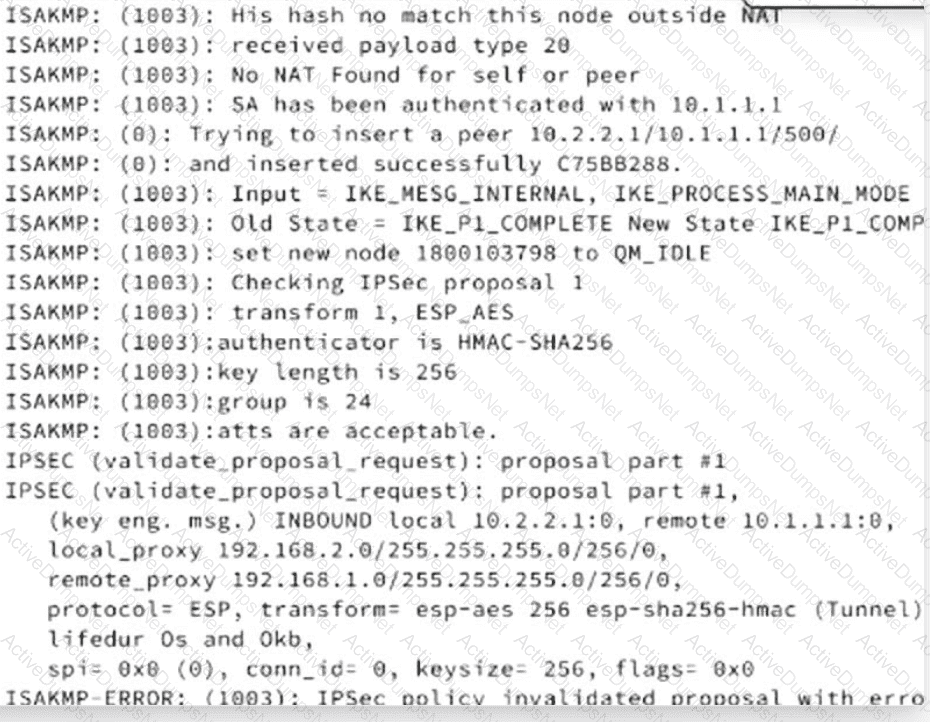
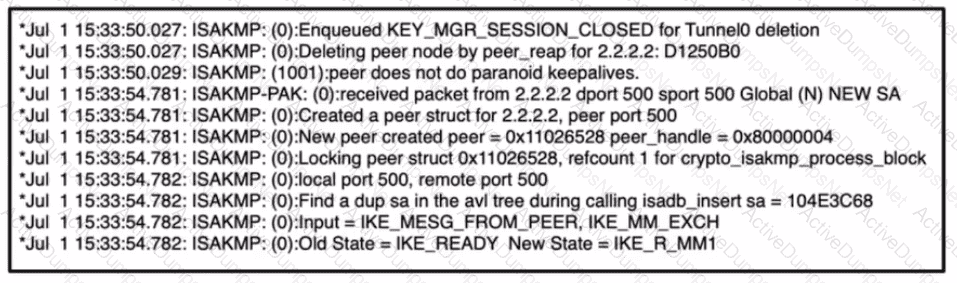
Refer to the exhibit.
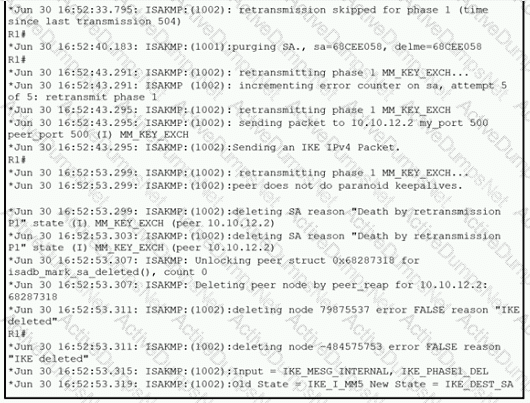
A network administrator configured a site-to-site VPN tunnel between two Cisco IOS routers, and hosts are unable to communicate between two sites of VPN. The network administrator runs the debug crypto isakmp sa command to track VPN status. What is the problem according to this command output?
Which two protocols must be configured to authenticate end users to the Cisco WSA? (Choose two.)
Which function is the primary function of Cisco AMP threat Grid?
Which two features are used to configure Cisco ESA with a multilayer approach to fight viruses and malware?
(Choose two)
An engineer needs to configure an access control policy rule to always send traffic for inspection without
using the default action. Which action should be configured for this rule?
Which capability is provided by application visibility and control?
Which license is required for Cisco Security Intelligence to work on the Cisco Next Generation Intrusion
Prevention System?
Which telemetry data captures variations seen within the flow, such as the packets TTL, IP/TCP flags, and payload length?
Which Cisco cloud security software centrally manages policies on multiple platforms such as Cisco ASA, Cisco Firepower, Cisco Meraki, and AWS?
What does the Cloudlock Apps Firewall do to mitigate security concerns from an application perspective?
What can be integrated with Cisco Threat Intelligence Director to provide information about security threats,
which allows the SOC to proactively automate responses to those threats?
How does Cisco Workload Optimization Manager help mitigate application performance issues?
Which process is used to obtain a certificate from a CA?
Which industry standard is used to integrate Cisco ISE and pxGrid to each other and with other
interoperable security platforms?
An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites
but other sites are not accessible due to an error. Why is the error occurring?
When network telemetry is implemented, what is important to be enabled across all network infrastructure devices to correlate different sources?
An engineer is implementing NAC for LAN users on a segmented network. The engineer confirms that the device of each user is supported and the Cisco switch configuration is correct.
Which configuration should be made next to ensure there are no authentication issues?
What must be configured in Cisco ISE to enforce reauthentication of an endpoint session when an endpoint is
deleted from an identity group?
Refer to the exhibit.
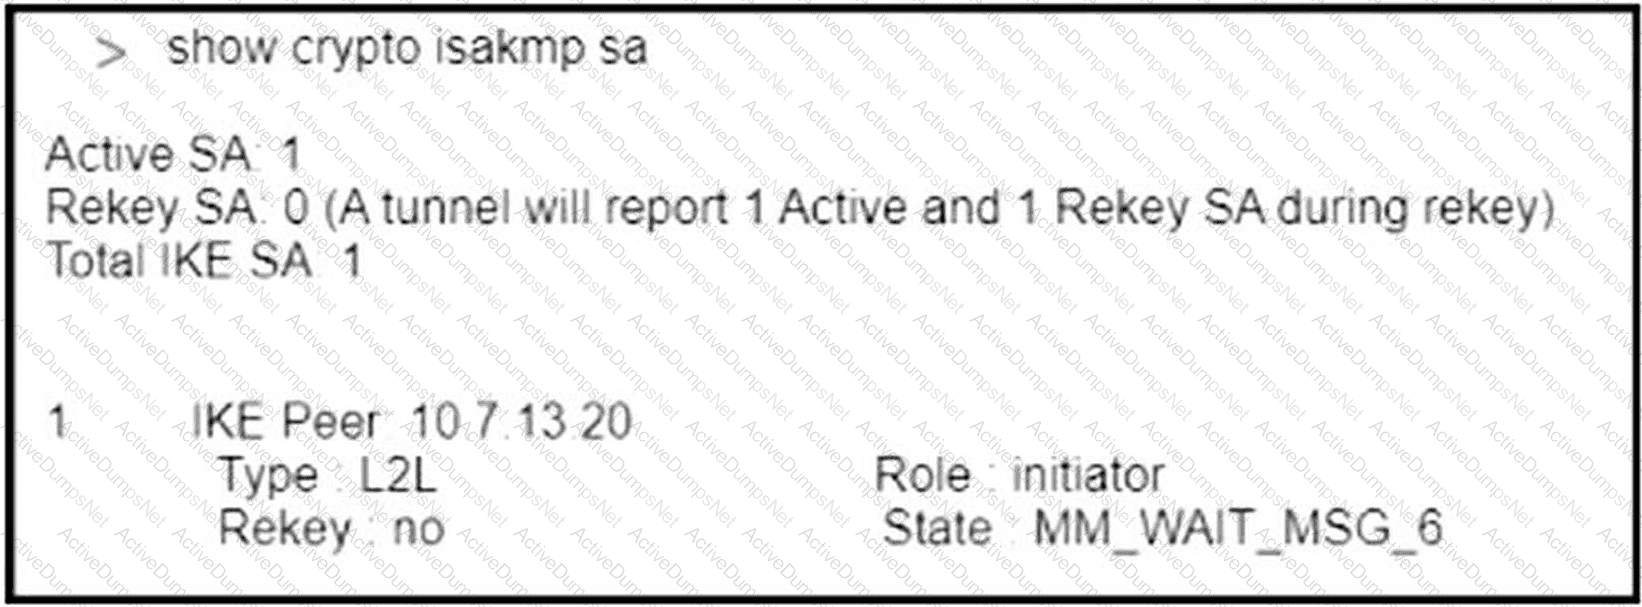
During the rollout of a new site-to-site VPN between a headquarters Cisco Secure Firewall Threat Defense device and a partner firewall, the tunnel never completes IKEv1 Phase 1 and remains in the MM_WAIT_MSG_6 state. Reachability between the firewalls over the Internet is verified, ISAKMP UDP port 500 is permitted end-to-end, and the IKE Phase 1 policy parameters—including encryption, hashing, DH group, and lifetime—match exactly on both ends. Which configuration action must be performed to resolve the issue?
Which technology must De used to Implement secure VPN connectivity among company branches over a private IP cloud with any-to-any scalable connectivity?
What is an attribute of Cisco Talos?
What is the process of performing automated static and dynamic analysis of files against preloaded
behavioral indicators for threat analysis?
A security engineer must create a policy based on the reputation verdict of a file from a Cisco Secure Email Gateway. The file with an undetermined verdict must be dropped. Which action must the security engineer take to meet the requirement?
How does a WCCP-configured router identify if the Cisco WSA is functional?
Which security principle advocates rapid cryptographic algorithm replacement to defend against quantum-computing threats?
Which solution supports high availability in routed or transparent mode as well as in northbound and
southbound deployments?
How does Cisco Umbrella archive logs to an enterprise owned storage?
Which technology reduces data loss by identifying sensitive information stored in public computing
environments?
Refer to the exhibit.
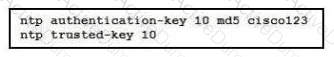
A network engineer is testing NTP authentication and realizes that any device synchronizes time with this router and that NTP authentication is not enforced What is the cause of this issue?
Which proxy mode must be used on Cisco WSA to redirect TCP traffic with WCCP?
How is Cisco Umbrella configured to log only security events?
Which DoS attack uses fragmented packets in an attempt to crash a target machine?
What are two characteristics of Cisco DNA Center APIs? (Choose two)
What is an advantage of network telemetry over SNMP pulls?
A network administrator needs to find out what assets currently exist on the network. Third-party systems need to be able to feed host data into Cisco Firepower. What must be configured to accomplish this?
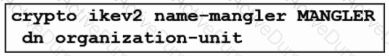
Refer to the exhibit. An engineer is implementing a certificate-based VPN. What is the result of the existing configuration?
Refer to the exhibit.
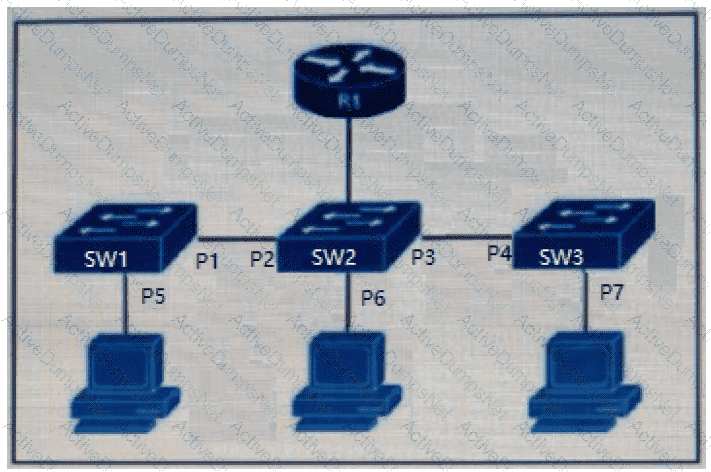
The DHCP snooping database resides on router R1, and dynamic ARP inspection is configured only on switch SW2. Which ports must be configured as untrusted so that dynamic ARP inspection operates normally?
What is a functional difference between a Cisco ASA and a Cisco IOS router with Zone-based policy firewall?
Which API technology with SDN architecture is used to communicate with a controller and network devices such as routers and switches?
An engineer is securing access to data served by a cloud-based application. The data must be protected from modification in transit, and its integrity must be validated. The following security measures have been implemented:
• Governance with role-based access control based on the principle of least privilege
• TLS 1.3 with signed certificates
• AES-256 with MD5
What must be configured to complete the secure implementation?
Why is it important to have a patching strategy for endpoints?
Refer to the exhibit.
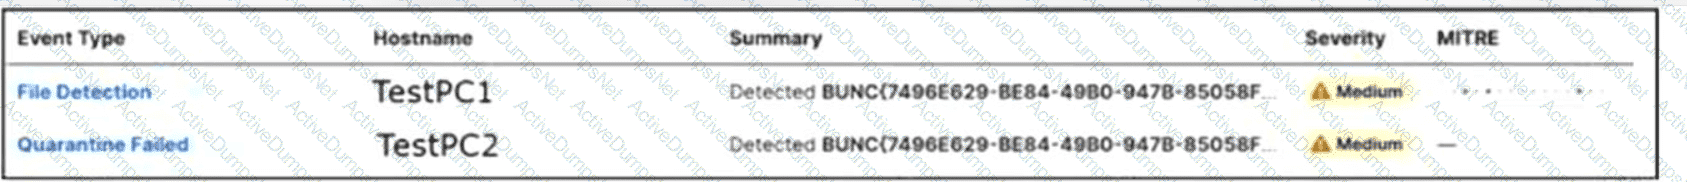
A Cisco Secure Endpoint malware event shows that a file was convicted as malicious and that its remediation status is Quarantine Failed. Before escalating the incident, the analyst must determine what can be concluded from the available event data. What is occurring based on the logs?
Which action configures the IEEE 802.1X Flexible Authentication feature lo support Layer 3 authentication mechanisms?
Which Cisco product provides proactive endpoint protection and allows administrators to centrally manage the
deployment?
What are two ways that Cisco Container Platform provides value to customers who utilize cloud service providers? (Choose two.)
How does a cloud access security broker function?
Which key feature of Cisco ZFW is unique among other Cisco IOS firewall solutions?
DoS attacks are categorized as what?
How many interfaces per bridge group does an ASA bridge group deployment support?
What is a benefit of using GET VPN over FlexVPN within a VPN deployment?
Which flaw does an attacker leverage when exploiting SQL injection vulnerabilities?
What are the two most commonly used authentication factors in multifactor authentication? (Choose two)
Which exfiltration method does an attacker use to hide and encode data inside DNS requests and queries?
Which Cisco command enables authentication, authorization, and accounting globally so that CoA is supported on the device?
II
An engineer musí set up 200 new laptops on a network and wants to prevent the users from moving their laptops around to simplify administration Which switch port MAC address security setting must be used?
What is the purpose of threat intelligence in the Cisco Security Reference Architecture?
A logistics company issues corporate laptops that must automatically establish a Cisco Secure Client VPN tunnel whenever users are outside the office and connected to an untrusted external network. Cisco Secure Firewall Threat Defense is the VPN headend and is already configured with remote-access profiles, address pools, and a PKI that distributes both machine and user certificates to endpoints. Management requires the tunnel to come up unattended before any user signs in to a laptop. Device-based authentication must be used, and the client must distinguish the corporate LAN from outside networks. The VPN must be connected when a user is outside the corporate network. Which configuration action must be performed to meet the requirements?
Which feature is used in a push model to allow for session identification, host reauthentication, and session termination?
Which MDM configuration provides scalability?
How does Cisco AMP for Endpoints provide next-generation protection?
Which two request of REST API are valid on the Cisco ASA Platform? (Choose two)
Which solution should be leveraged for secure access of a CI/CD pipeline?
Which two global commands must the network administrator implement to limit the attack surface of an internet-facing Cisco router? (Choose two.)
Refer to the exhibit.
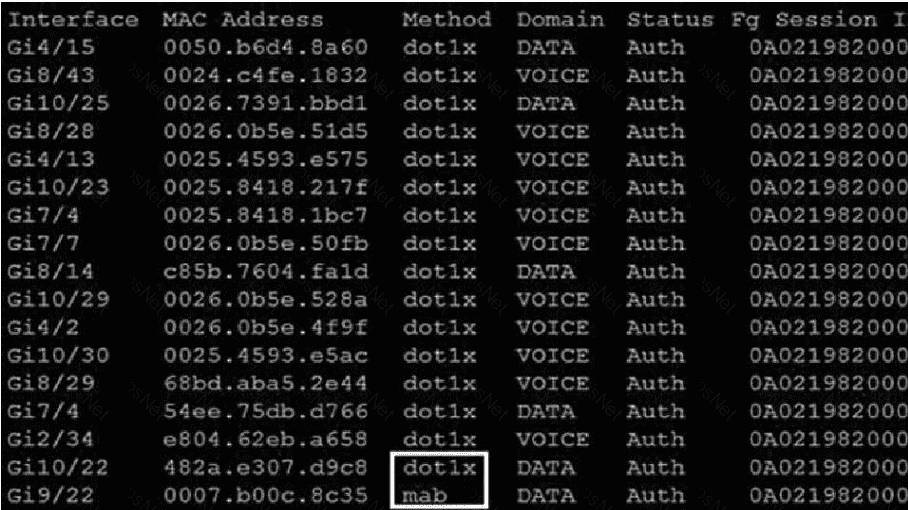
Which command was used to generate this output and to show which ports are
authenticating with dot1x or mab?
A web hosting company must upgrade its older, unsupported on-premises servers. The company wants a cloud solution in which the cloud provider is responsible for:
Server patching
Application maintenance
Data center security
Disaster recovery
Which type of cloud meets the requirements?
An engineer enabled SSL decryption for Cisco Umbrella intelligent proxy and needs to ensure that traffic is inspected without alerting end-users.
What is a benefit of using Cisco Tetration?
What is a feature of NetFlow Secure Event Logging?
How is data sent out to the attacker during a DNS tunneling attack?
In which situation should an Endpoint Detection and Response solution be chosen versus an Endpoint
Protection Platform?
What provides visibility and awareness into what is currently occurring on the network?
Refer to the exhibit.
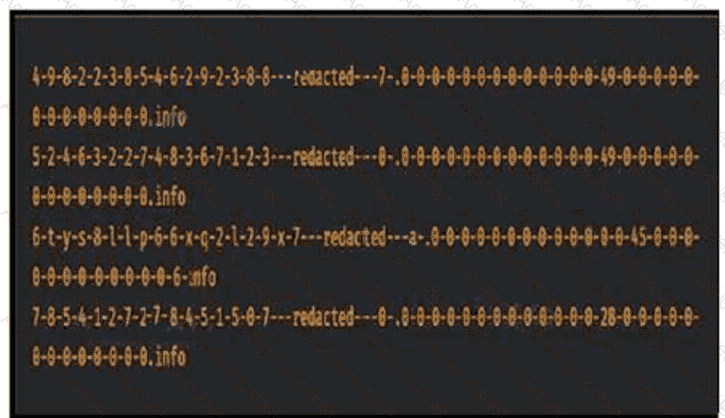
Consider that any feature of DNS requests, such as the length off the domain name
and the number of subdomains, can be used to construct models of expected behavior to which
observed values can be compared. Which type of malicious attack are these values associated with?
Which Cisco firewall solution supports configuration via Cisco Policy Language?
An engineer configured a new network identity in Cisco Umbrella but must verify that traffic is being routed
through the Cisco Umbrella network. Which action tests the routing?
Which type of data does the Cisco Stealthwatch system collect and analyze from routers, switches, and firewalls?
An engineer is configuring their router to send NetfFow data to Stealthwatch which has an IP address of 1 1 11 using the flow record Stea!thwatch406397954 command Which additional command is required to complete the flow record?
Which two criteria must a certificate meet before the WSA uses it to decrypt application traffic? (Choose two.)
Which solution allows an administrator to provision, monitor, and secure mobile devices on Windows and Mac computers from a centralized dashboard?
Which attack type attempts to shut down a machine or network so that users are not able to access it?
Which service allows a user export application usage and performance statistics with Cisco Application Visibility
and control?
A large organization wants to deploy a security appliance in the public cloud to form a site-to-site VPN
and link the public cloud environment to the private cloud in the headquarters data center. Which Cisco
security appliance meets these requirements?
An engineer is configuring Cisco WSA and needs to deploy it in transparent mode. Which configuration component must be used to accomplish this goal?
What are two list types within AMP for Endpoints Outbreak Control? (Choose two)
What are two functionalities of northbound and southbound APIs within Cisco SDN architecture? (Choose two.)
Which two request methods of REST API are valid on the Cisco ASA Platform? (Choose two.)
Which two Cisco ISE components must be configured for BYOD? (Choose two.)
With which components does a southbound API within a software-defined network architecture communicate?
Which two conditions are prerequisites for stateful failover for IPsec? (Choose two)
A network administrator is modifying a remote access VPN on an FTD managed by an FMC. The administrator wants to offload traffic to certain trusted domains. The administrator wants this traffic to go out of the client ' s local internet and send other internet-bound traffic over the VPN Which feature must the administrator configure?
An engineer must modify an existing remote access VPN using a Cisco AnyConnect Secure Mobility client solution and a Cisco Secure Firewall. Currently, all the traffic generate by the user Is sent to the VPN tunnel and the engineer must now exclude some servers and access them directly instead. Which element must be modified to achieve this goat?
Which Cisco platform provides an agentless solution to provide visibility across the network including encrypted traffic analytics to detect malware in encrypted traffic without the need for decryption?
Which benefit does DMVPN provide over GETVPN?
An email administrator is setting up a new Cisco ESA. The administrator wants to enable the blocking of greymail for the end user. Which feature must the administrator enable first?
Which two functions does the Cisco Advanced Phishing Protection solution perform in trying to protect from phishing attacks? (Choose two.)
An engineer must implement an external application that authenticates against the Cisco Secure Email Threat Defense API to perform automated message searches. The application already presents a user bearer token, but the API requires an additional authentication header with each request. The engineer must configure the external application to include the required header alongside the bearer token so that the API calls are accepted. Which header must be configured?
Which feature enables a Cisco ISR to use the default bypass list automatically for web filtering?
Which term describes when the Cisco Secure Firewall downloads threat intelligence updates from Cisco Tables?
A healthcare organization is deploying Cisco Secure Access to prevent protected health information from being shared with generative AI services. The security team requires real-time DLP inspection only for traffic destined for AI applications, with minimal false positives during general web browsing. The policy must permit tuning based on the proximity and match counts of PHI identifiers. Which configuration action must the engineer perform?
Which feature requires that network telemetry be enabled?
An engineer notices traffic interruption on the network. Upon further investigation, it is learned that broadcast
packets have been flooding the network. What must be configured, based on a predefined threshold, to
address this issue?
Which two types of policies are used by ZTNA to provide access to an application? (Choose two.)
What are two workloaded security models? (Choose two)
Which two solutions help combat social engineering and phishing at the endpoint level? (Choose two.)
In a federated single sign-on environment, which protocol exchanges XML-based assertions between an identity provider and a service provider for authentication?
A security engineer requires social-media websites to be blocked through Cisco Secure Firewall Threat Defense. Which configuration action must the engineer apply to meet the requirement?
An engineer must implement a file transfer solution between a company ' s data center and branches. The company has numerous servers hosted in a hybrid cloud implementation. The file transfer protocol must support authentication, protect the data against unauthorized access, and ensure that users cannot list directories or remove files remotely. Which protocol must be used?
What is a feature of an endpoint detection and response solution?
An organization recently installed a Cisco WSA and would like to take advantage of the AVC engine to allow the organization to create a policy to control application specific activity. After enabling the AVC engine, what must be done to implement this?
What limits communication between applications or containers on the same node?
What are two workload security models? (Choose two.)
Which algorithm is an NGE hash function?
Which two parameters are used to prevent a data breach in the cloud? (Choose two.)
What is a benefit of using Cisco Umbrella?
What are two benefits of workload security? (Choose two.)
Which Cisco solution integrates industry-leading artificial intelligence and machine learning analytics and an assurance database to review the security posture and maintain visibility of an organization’s cloud environment?
Which ESA implementation method segregates inbound and outbound email?
An engineer is configuring cloud logging on Cisco ASA and needs events to compress. Which component must be configured to accomplish this goal?
An engineer is deploying a Cisco Secure Email Gateway and must configure a sender group that decides which mail policy will process the mail. The configuration must accept incoming mails and relay the outgoing mails from the internal server. Which component must be configured to accept the connection to the listener and meet these requirements on a Cisco Secure Email Gateway?
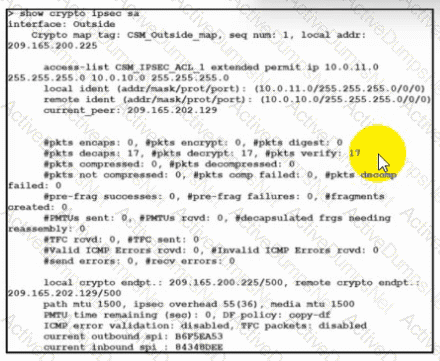
Refer to the exhibit. Traffic is not passing through IPsec site-to-site VPN on the Secure Firewall Threat Defense appliance. What is causing this issue?
What is a characteristic of an EDR solution and not of an EPP solution?
Which component of Cisco umbrella architecture increases reliability of the service?
Which CoA response code is sent if an authorization state is changed successfully on a Cisco IOS device?
An organization received a large amount of SPAM messages over a short time period. In order to take action on the messages, it must be determined how harmful the messages are and this needs to happen dynamically.
What must be configured to accomplish this?
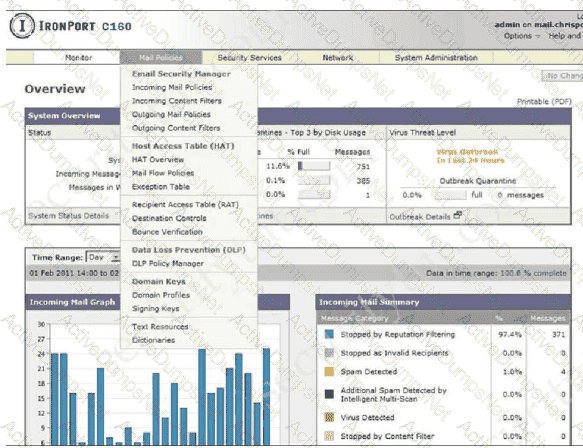
When a transparent authentication fails on the Web Security Appliance, which type of access does the end user get?
Which two activities are performed using Cisco Catalyst Center? (Choose two.)
A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256
cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?
Refer to the exhibit.
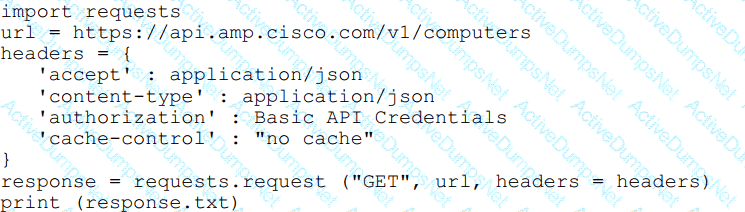
What will happen when this Python script is run?
Which metric is used by the monitoring agent to collect and output packet loss and jitter information?
Which service allows a user to export application usage and performance statistics with Cisco Application Visibility and Control?
Which two characteristics of messenger protocols make data exfiltration difficult to detect and prevent?
(Choose two)
Which two products are used to forecast capacity needs accurately in real time? (Choose two.)
Which Cisco platform onboards the endpoint and can issue a CA signed certificate while also automatically configuring endpoint network settings to use the signed endpoint certificate, allowing the endpoint to gain network access?
Which solution stops unauthorized access to the system if a user ' s password is compromised?
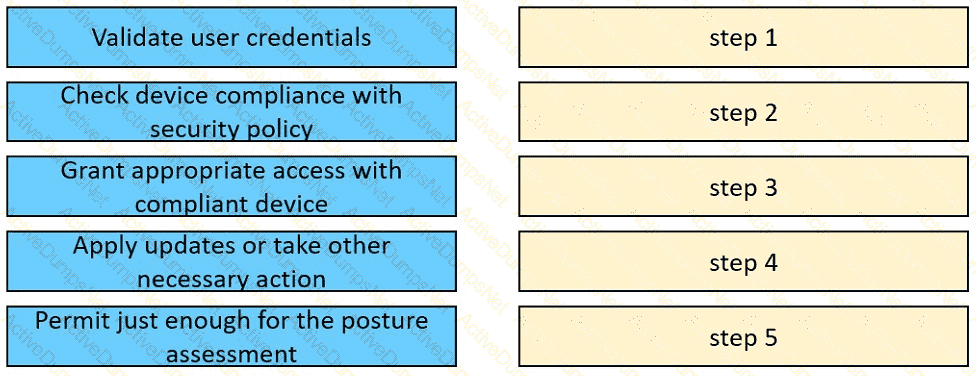
Drag and drop the posture assessment flow actions from the left into a sequence on the right.
Which two prevention techniques are used to mitigate SQL injection attacks? (Choose two)
An engineer is configuring cloud logging using a company-managed Amazon S3 bucket for Cisco Umbrella logs. What benefit does this configuration provide for accessing log data?
An engineer is trying to decide whether to use Cisco Umbrella, Cisco CloudLock, Cisco Stealthwatch, or Cisco AppDynamics Cloud Monitoring for visibility into data transfers as well as protection against data exfiltration Which solution best meets these requirements?
Which Cisco solution provides a comprehensive view of Internet domains. IP addresses, and autonomous systems to help pinpoint attackers and malicious infrastructures?
What is the purpose of a NetFlow version 9 template record?
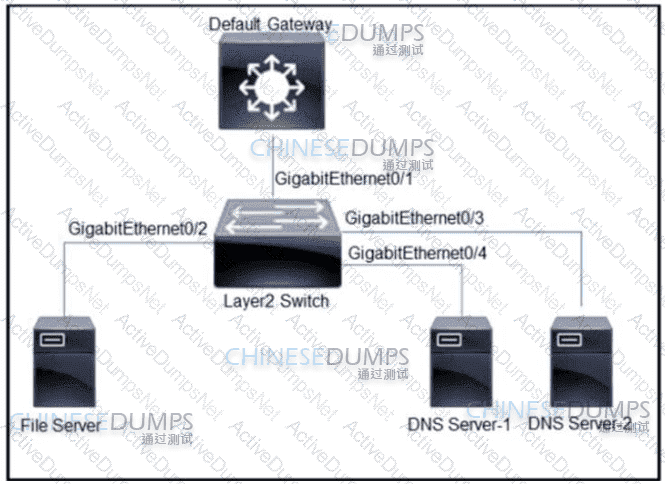
Refer to the exhibit. All servers are in the same VLAN/Subnet. DNS Server-1 and DNS Server-2 must communicate with each other, and all servers must communicate with default gateway multilayer switch. Which type of private VLAN ports should be configured to prevent communication between DNS servers and the file server?
A Cisco ESA network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Cisco ESA is not dropping files that have an undetermined verdict. What is causing this issue?
Which method of attack is used by a hacker to send malicious code through a web application to an unsuspecting user to request that the victim ' s web browser executes the code?
Which option is the main function of Cisco Firepower impact flags?
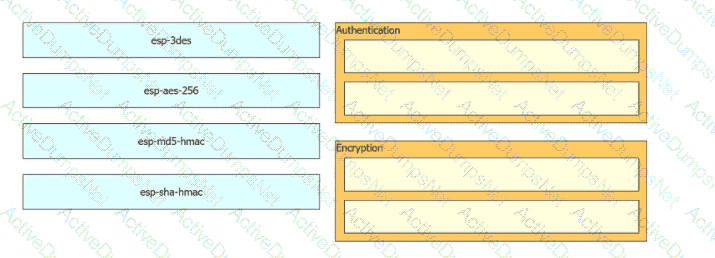
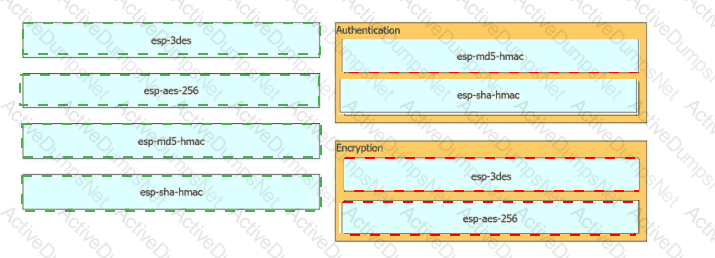
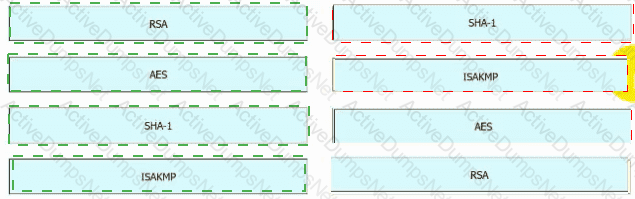
Drag and drop the cryptographic algorithms for IPsec from the left onto the cryptographic processes on the right.
Refer to the exhibit.
aaa new-model
aaa authentication dot1x default group ISE-SERVERS
aaa authorization network default group ISE-SERVERS
aaa accounting dot1x default start-stop group ISE-SERVERS
!
radius server RADIUS_SRV
address ipv4 172.16.10.12 auth-port 1812 acct-port 1813
key shared-secret C1sc0123
!
aaa group server radius ISE-SERVERS
server name RADIUS_SRV
radius-server vsa send authentication
radius-server vsa send accounting
radius-server attribute 6 on-for-login-auth
radius-server attribute 8 include-in-access-req
radius-server attribute 25 access-request include
ip device tracking
!
interface range GigabitEthernet1/0/1 - 48
switchport
switchport host
authentication priority dot1x mab
authentication order dot1x mab
A security engineer is integrating a new Cisco Catalyst access switch with Cisco ISE to enforce port-based network access control using 802.1X. The AAA RADIUS server group and access interfaces are configured on the Cisco Catalyst switch. Cisco ISE has authentication and authorization policies, the workstation supplicants are configured as expected, and connectivity between the switch and ISE is working. During testing, the workstations fail to trigger authentication sessions, and no RADIUS requests appear in the ISE logs or on the switch interfaces. Which two configuration commands must be added to the Cisco Catalyst switch? (Choose two.)
A large enterprise is currently managing a hybrid environment consisting of a private data center and multiple public cloud providers. The security engineering team is concerned about “Shadow IT” and the lack of visibility into unauthorized cloud services being used by various departments. The architect must select a solution that provides comprehensive discovery of cloud application usage and assesses the risk of each service based on industry certifications. Which technical solution must be used to provide cross-environment visibility?
What do tools like Jenkins, Octopus Deploy, and Azure DevOps provide in terms of application and
infrastructure automation?
A network engineer is tasked with configuring a Cisco ISE server to implement external authentication against Active Directory. What must be considered about the authentication requirements? (Choose two.)
Which attribute has the ability to change during the RADIUS CoA?
A networking team must harden an organization ' s network from VLAN hopping attacks. The team disables Dynamic Trunking Protocol and puts any unused ports in an unused VLAN. A trunk port is used as a trunk link. What must the team configure next to harden the network against VLAN hopping attacks?
What are two differences between a Cisco Secure Web Appliance that is running in transparent mode and one running in explicit mode? (Choose two.)
In which two ways does the Cisco Advanced Phishing Protection solution protect users? (Choose two.)
Which type of information does threat intelligence gather to identify potential threats using common adversary techniques?
A network administrator is setting up Cisco FMC to send logs to Cisco Security Analytics and Logging (SaaS). The network administrator is anticipating a high volume of logging events from the firewalls and wants lo limit the strain on firewall resources. Which method must the administrator use to send these logs to Cisco Security Analytics and Logging?
What is an advantage of the Cisco Umbrella roaming client?
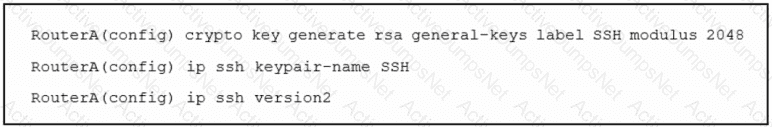
Refer to the exhibit. An engineer must enable secure SSH protocols and enters this configuration. What are two results of running this set of commands on a Cisco router? (Choose two.)
Which standard is used to automate exchanging cyber threat information?
Which solution is more secure than the traditional use of a username and password and encompasses at least two of the methods of authentication?
An engineer is configuring Cisco Secure Endpoint to enhance security by preventing the execution of certain files by users. The engineer needs to ensure that the specific executable file name Cisco_Software_0505446151.exe is blocked from running while never being quarantined. What must the engineer configure to meet the requirement?
How does Cisco Umbrella protect clients when they operate outside of the corporate network?
Which feature is supported when deploying Cisco ASAv within AWS public cloud?
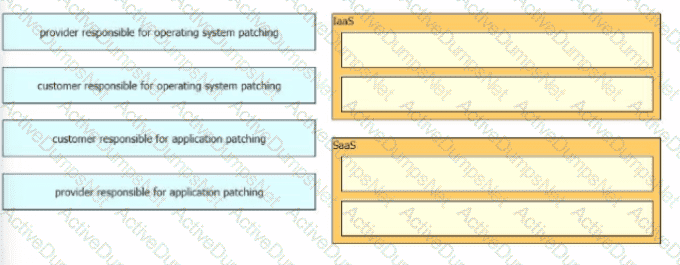
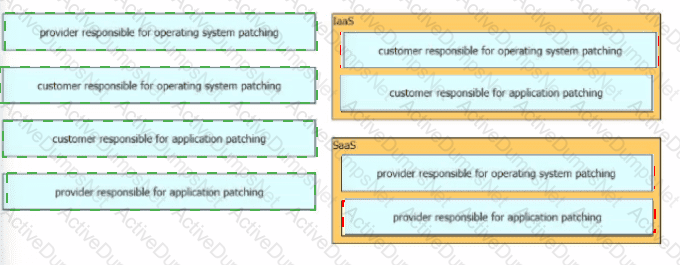
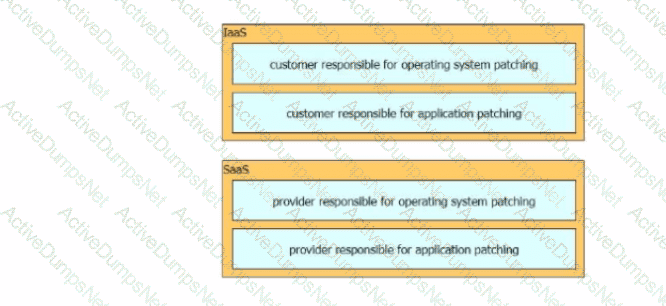
Drag and drop the security responsibilities from the left onto the corresponding cloud service models on the right.
What is the purpose of the Trusted Automated exchange cyber threat intelligence industry standard?
A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:
Matching IKEv2 proposals, preshared keys, and IPsec transform sets
Access control rules permitting the traffic
Crypto maps applied to the outside interfaces
VPN traffic exempted from inspection
During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?
Using Cisco Firepower’s Security Intelligence policies, upon which two criteria is Firepower block based?
(Choose two)
What are two reasons for implementing a multifactor authentication solution such as Duo Security provide to an
organization? (Choose two)
A security engineer must configure a Splunk Universal Forwarder to send network traffic logs from Cisco Catalyst switches to a Splunk indexer cluster. Strict compliance requirements require all network traffic logs to be ingested into Splunk as an audit trail. The environment includes thousands of forwarders, and the data must be distributed across all indexers. Which two configuration actions must be performed? (Choose two.)
A hacker initiated a social engineering attack and stole username and passwords of some users within a company. Which product should be used as a solution to this problem?
An organization wants to secure users, data, and applications in the cloud. The solution must be API-based and
operate as a cloud-native CASB. Which solution must be used for this implementation?
An engineer implements Cisco CloudLock to secure a Microsoft Office 365 application in the cloud. The engineer must configure protection for corporate files in case of any incidents. Which two actions must be taken to complete the implementation? (Choose two.)
A switch with Dynamic ARP Inspection enabled has received a spoofed ARP response on a trusted interface.
How does the switch behave in this situation?
Which protocol provides the strongest throughput performance when using Cisco AnyConnect VPN?
Which Cisco security solution determines if an endpoint has the latest OS updates and patches installed on the system?
Refer to the exhibit.
An engineer configures an IPsec VPN between two Cisco Secure Firewall Threat Defense devices named FTD1 and FTD2. However, the hosts behind FTD1 and FTD2 cannot communicate with each other. The engineer runs a debug command to troubleshoot the issue. What must be configured to resolve the issue?
What are two Trojan malware attacks? (Choose two)
Which problem Is solved by deploying a multicontext firewall?
When Cisco and other industry organizations publish and inform users of known security findings and
vulnerabilities, which name is used?
When web policies are configured in Cisco Umbrella, what provides the ability to ensure that domains are blocked when they host malware, command and control, phishing, and more threats?
Which solution combines Cisco IOS and IOS XE components to enable administrators to recognize
applications, collect and send network metrics to Cisco Prime and other third-party management tools, and prioritize application traffic?
Which type of DNS abuse exchanges data between two computers even when there is no direct connection?
What provides total management for mobile and PC including managing inventory and device tracking, remote view, and live troubleshooting using the included native remote desktop support?
Which security solution uses NetFlow to provide visibility across the network, data center, branch offices, and cloud?
Drag and drop the Cisco CWS redirection options from the left onto the capabilities on the right.
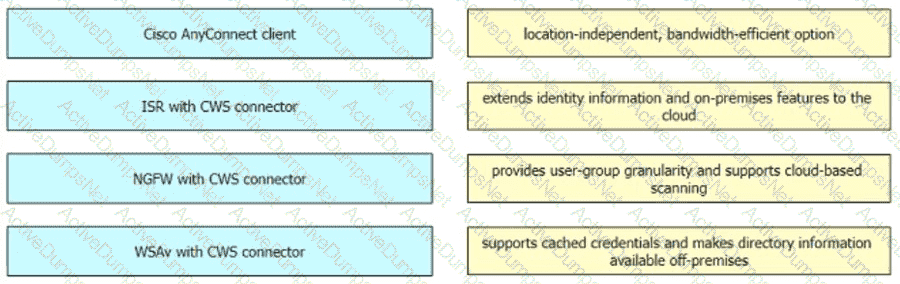
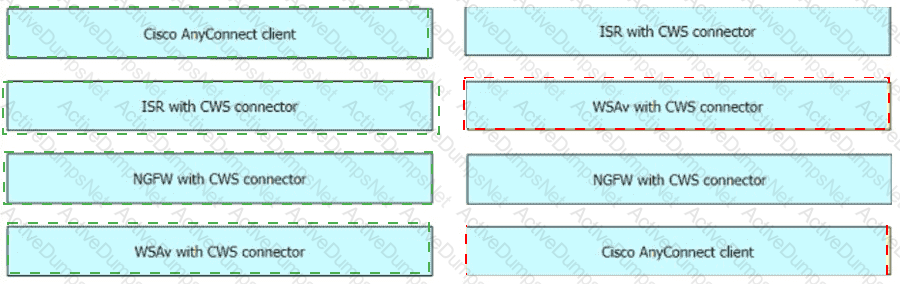
An organization has a Cisco ESA set up with policies and would like to customize the action assigned for
violations. The organization wants a copy of the message to be delivered with a message added to flag it as a
DLP violation. Which actions must be performed in order to provide this capability?
A network administrator is using the Cisco ESA with AMP to upload files to the cloud for analysis. The network
is congested and is affecting communication. How will the Cisco ESA handle any files which need analysis?
Which network monitoring solution uses streams and pushes operational data to provide a near real-time view
of activity?
In an IaaS cloud services model, which security function is the provider responsible for managing?
A company has 5000 Windows users on its campus. Which two precautions should IT take to prevent WannaCry ransomware from spreading to all clients? (Choose two.)
What are two benefits of using Cisco Secure Access Secure Web Gateway in addition to DNS-layer protection? (Choose two.)
Which two capabilities of Integration APIs are utilized with Cisco Catalyst Center? (Choose two.)
Refer to the exhibit.
What is a result of the configuration?
Which two actions does the Cisco identity Services Engine posture module provide that ensures endpoint security?(Choose two.)
Drag and drop the VPN functions from the left onto the description on the right.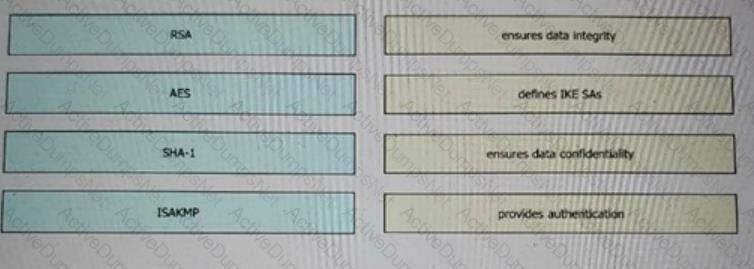
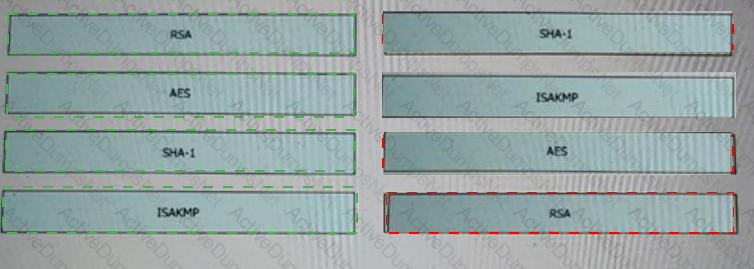
An engineer needs behavioral analysis to detect malicious activity on the hosts, and is configuring the
organization’s public cloud to send telemetry using the cloud provider’s mechanisms to a security device. Which
mechanism should the engineer configure to accomplish this goal?
An organization wants to implement a cloud-delivered and SaaS-based solution to provide visibility and threat detection across the AWS network. The solution must be deployed without software agents and rely on AWS VPC flow logs instead. Which solution meets these requirements?
Which type of attack is MFA an effective deterrent for?
An engineer is configuring Dropbox integration with Cisco Cloudlock. Which action must be taken before granting API access in the Dropbox admin console?
Which policy represents a shared set of features or parameters that define the aspects of a managed device that are likely to be similar to other managed devices in a deployment?
Refer to the exhibit. When creating an access rule for URL filtering, a network engineer adds certain categories and individual URLs to block. What is the result of the configuration?
Which two devices support WCCP for traffic redirection? (Choose two.)
Which functionality does Incident Manager provide in Cisco XDR?
Refer to the exhibit,
which command results in these messages when attempting to troubleshoot an iPsec VPN connection?
Which two methods must be used to add switches into the fabric so that administrators can control how switches are added into DCNM for private cloud management? (Choose two.)
A security engineer is tasked with configuring TACACS on a Cisco ASA firewall. The engineer must be able to access the firewall command line interface remotely. The authentication must fall back to the local user database of the Cisco ASA firewall. AAA server group named TACACS-GROUP is already configured with TACACS server IP address 192.168.10.10 and key C1sc0512222832!. Which configuration must be done next to meet the requirement?
What is a feature of the open platform capabilities of Cisco DNA Center?
Which solution offers automated blocking of known threats and visibility into zero-day attack behavior, with the ability to respond directly from the console?
After deploying a Cisco ESA on your network, you notice that some messages fail to reach their destinations.
Which task can you perform to determine where each message was lost?
An engineer must deploy Cisco Secure Email with Cloud URL Analysis and must meet these requirements:
To protect the network from large-scale virus outbreaks
To protect the network from non-viral attacks such as phishing scams and malware distribution
To provide active analysis of the structure of the URL and information about the domain and page contents
Which two prerequisites must the engineer ensure are configured? (Choose two.)
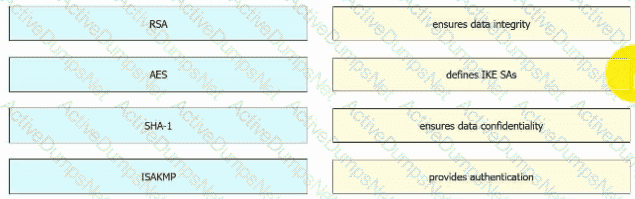
Drag and drop the VPN functions from the left onto the descriptions on the right.
A network engineer must enable DHCP snooping on the corporate switches only for VLAN 2. Management requires DHCP traffic from unauthorized servers to be dropped. DHCP snooping is already enabled globally, and the uplink interface toward the authorized DHCP server is already trusted. Which configuration command must be applied to meet the requirement?
What is the difference between EPP and EDR?