Redeem Your Black Friday Code: 75% Off All Exam Bundles! Use coupon code below! - Ends in 0d 00h 00m 00s - Coupon code: discactive

Cisco 100-160 Cisco Certified Support Technician (CCST) Cybersecurity Exam Practice Test

Page: 1 / 7
Total 69 questions

Cisco Certified Support Technician (CCST) Cybersecurity Questions and Answers

Question 1

What is the main purpose of a disaster recovery plan as compared to a business continuity plan?

Options:

A.

Limiting operational downtime.

B.

Keeping the business open in some capacity during a disaster.

C.

Restoring data access and an IT infrastructure as quickly as possible.

D.

Allowing staff to continue to serve customers throughout a disaster.

Question 2

Several employees report that the company intranet website is no longer accepting their login credentials.

You attempt to access the site using its URL and notice several misspellings on the webpage. However, when you access the site directly using its IP address, it functions normally.

What should you do?

Options:

A.

Restore a backup copy of the authentication database.

B.

Verify the accuracy of the entry for the site in the local DNS server.

C.

Take the company web portal offline immediately.

D.

Update the web server software to the latest version.

Question 3

A threat actor sets up a rogue access point (AP) at a local cafe. The rogue AP captures traffic and then forwards the traffic to the cafe AP.

Which type of attack does this scenario describe?

Options:

A.

Reconnaissance

B.

Man-in-the-middle

C.

DDoS

D.

Ransomware

Question 4

Which security assessment of IT systems verifies that PII data is available, accurate, confidential, and accessible only by authorized users?

Options:

A.

Risk framing

B.

Cyber Kill Chain

C.

Workflow management

D.

Information assurance

Question 5

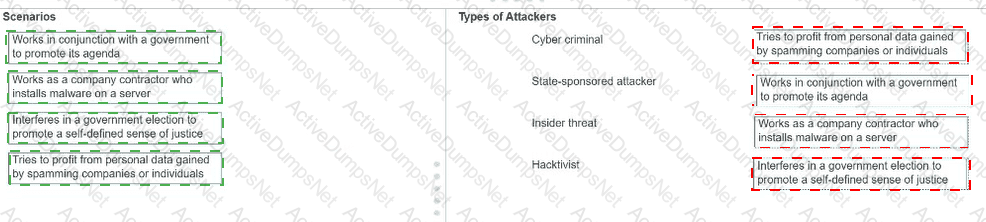
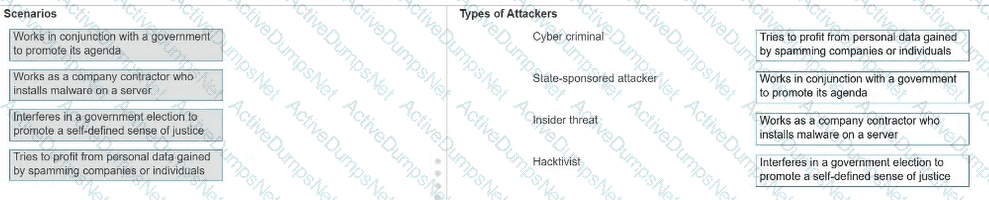
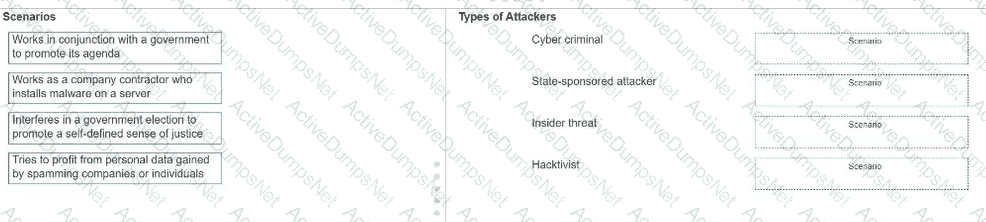
Move each scenario from the list on the left to the correct type of attacker on the right.

Note: You will receive partial credit for each correct answer.
Question # 5

Options:

Question 6

During an incident response, the security team needs to isolate a compromised server from the rest of the network but still allow forensic analysis. Which action should they take?

Options:

A.

Power off the server immediately.

B.

Disconnect the server from the network and connect it to an isolated forensic network.

C.

Delete suspicious files from the server.

D.

Reset all user passwords on the server.

Question 7

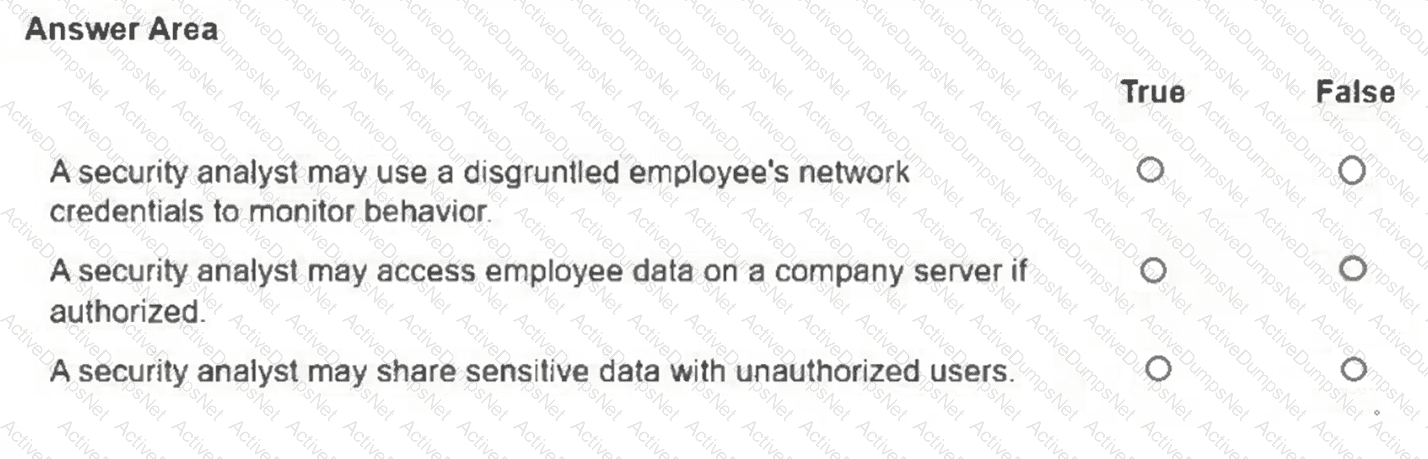
For each statement, select True if the statement adheres to the cybersecurity code of ethics, or False if it does not.

Note: You will receive partial credit for each correct selection.
Question # 7

Options:

Question 8

A remote worker is visiting a branch office to attend face-to-face meetings. The worker tries to associate their company laptop with the branch wireless access point (WAP) but is unable to do so.

What is a possible cause?

Options:

A.

The SSID is not broadcasting.

B.

The WAP is configured for MAC address filtering.

C.

The IP address of the laptop is not correct.

D.

The WAP is using open authentication.

Question 9

Which Windows app is a command-line interface that includes a sophisticated scripting language used to automate Windows tasks?

Options:

A.

PowerShell

B.

Microsoft Management Console

C.

Vim

D.

MS-DOS

Question 10

A security administrator is implementing defense-in-depth.

Which set of solutions applies protection across different layers of the defense-in-depth approach?

Options:

A.

IPS/IDS, endpoint detection and response (EDR) solutions, strong passwords, and a firewall

B.

IPS/IDS, antivirus/anti-malware, a firewall, and endpoint detection and response (EDR) solutions

C.

Identity and access management (IAM), encryption, IPS/IDS, and endpoint detection and response (EDR) solutions

D.

Strong passwords, access controls, MFA, and identity and access management (IAM)

Question 11

Which three authentication factors are valid for use in a multifactor authentication scenario? (Choose three.)

Note: You will receive partial credit for each correct selection.
Options:

A.

Something you have

B.

Something you are

C.

Something you know

D.

Something you do

E.

Something you earn

F.

Something you see

Question 12

To access your online banking account, you enter a strong password and then enter a five-digit verification code sent to your smartphone.

Which type of authentication does this situation describe?

Options:

A.

Multifactor

B.

VPN

C.

RADIUS

D.

AAA

Question 13

Why is it necessary to update firmware to the latest version?

Options:

A.

To support the latest operating systems and applications

B.

To patch firmware in the kernel of the operating system

C.

To correct security holes and weaknesses

D.

To explore new hardware features

Question 14

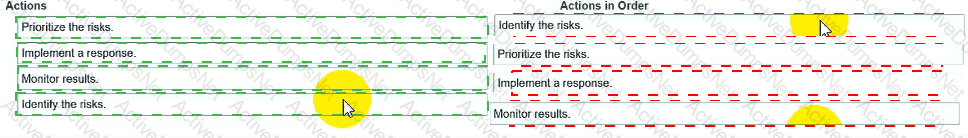
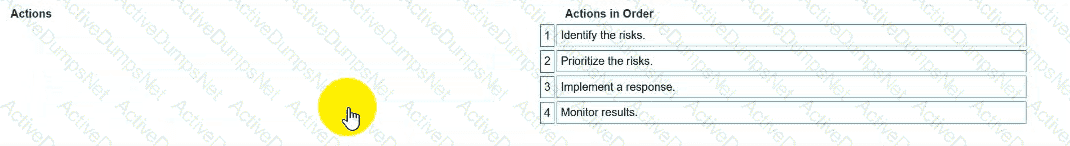
You need to manage security risks at your company. In which order should you complete the actions?

Move all the actions to the answer area and place them in the correct order.
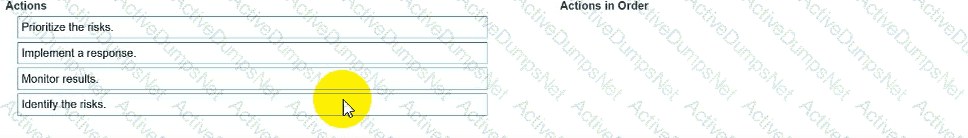
Question # 14

Options:

Question 15

A SOC analyst notices repeated failed login attempts from a foreign IP address followed by a successful login to a privileged account. What is the most appropriate next step?

Options:

A.

Reset the affected user’s password and investigate the scope of compromise.

B.

Block all foreign IP addresses from accessing the network.

C.

Run a full vulnerability scan of the corporate network.

D.

Ignore the event unless it happens again.

Question 16

Your supervisor tells you that you will participate in a CVSS assessment.

What will you be doing?

Options:

A.

Performing penetration tests on internal network devices and end systems

B.

Analyzing host logs to identify abnormal activities

C.

Interviewing users to determine their level of cybersecurity awareness

D.

Evaluating end system security and scoring software vulnerabilities

Question 17

What does hashing provide for data communication?

Options:

A.

Data non-repudiation

B.

Origin authentication

C.

Data encryption

D.

Data integrity

Question 18

A security assessment showed that a system administrator accessed files outside of normal working hours. The assessment listed the commands the administrator executed and indicated how long the administrator was connected to the system.

Which AAA component does this represent?

Options:

A.

Authorization

B.

Auditing

C.

Accounting

D.

Authentication

Question 19

Which macOS security feature encrypts the entire macOS volume?

Options:

A.

FileVault

B.

Gatekeeper

C.

System Integrity Protection (SIP)

D.

XProtect

Question 20

Which two private IPv4 addresses would be blocked on the Internet to prevent security and performance issues? (Choose two.)

Note: You will receive partial credit for each correct selection.

Options:

A.

203.0.113.168

B.

192.168.18.189

C.

224.0.2.172

D.

172.18.100.78

Page: 1 / 7
Total 69 questions